
Step 1. Create a New Certificate Template.
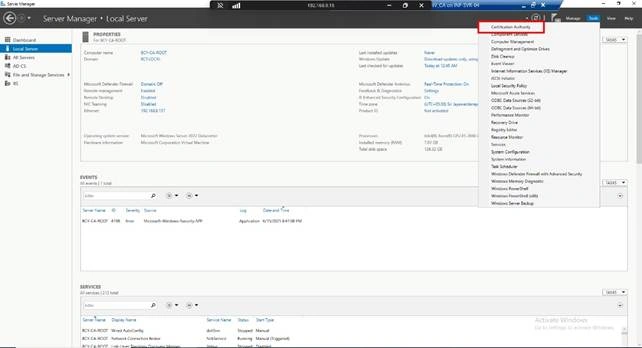
- Open Server Manager on the CA server and launch Certificate Authority.
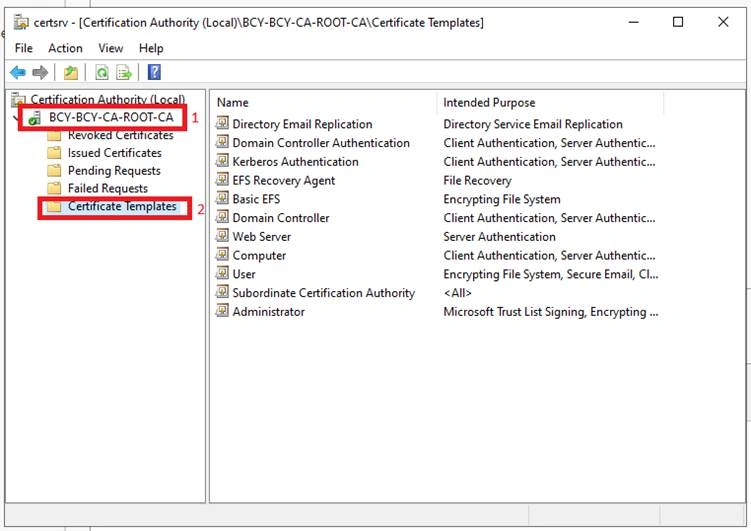
- Expand your CA server node and select Certificate Templates.
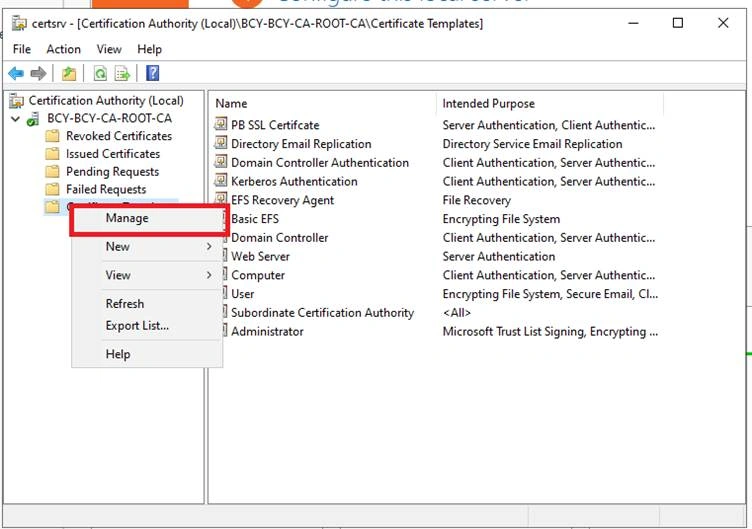
- Right-click on Certificate Templates and choose Manage.
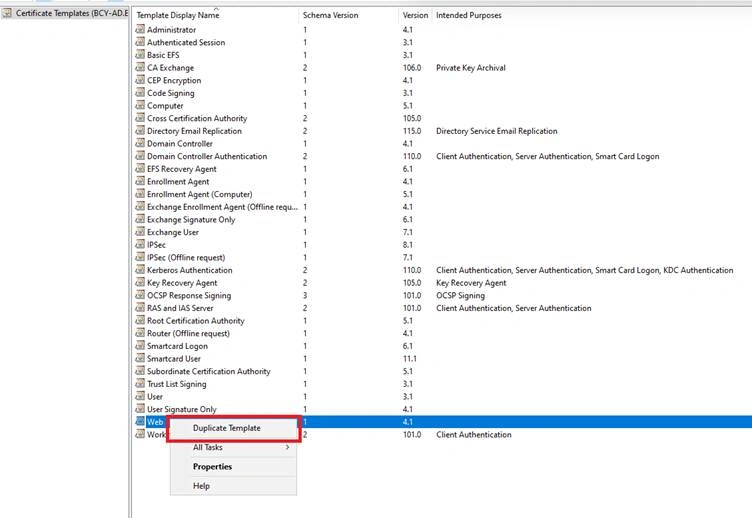
- In the Certificate Templates Console, locate the Web Server template, right-click it, and choose Duplicate Template.
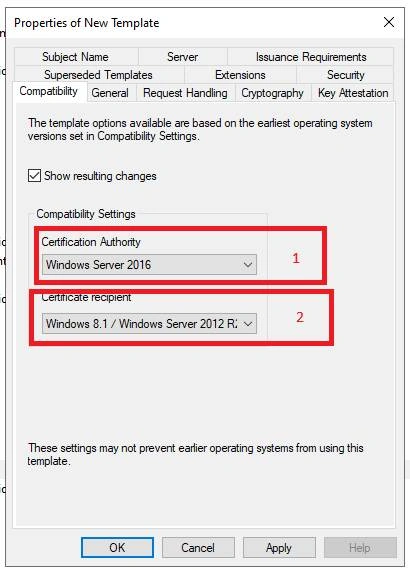
- A new window will pop up titled Properties of New Template. Configure the following:
1. Compatibility Tab
- Certification Authority: Select the latest version available.
- Certificate Recipient: Choose the version that matches your environment.
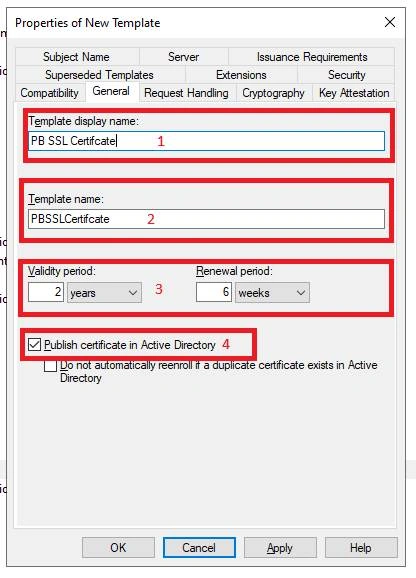
2. General Tab
- Template Display Name: Provide a clear, unique name.
- Template Name: Set a suitable template name.
- Validity Period: Configure according to your organization’s policy (default is 2 years).
- If your CA is Enterprise and domain-joined, check "Publish certificate in Active Directory."
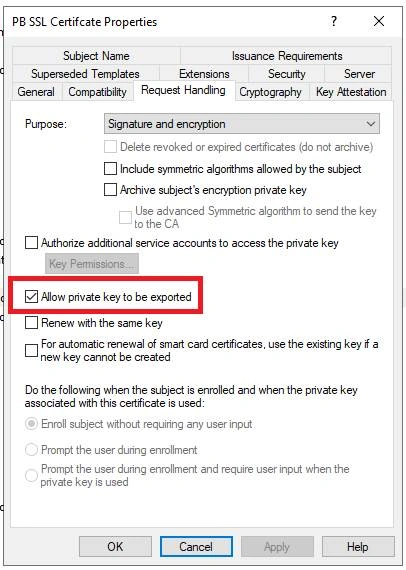
3. Request Handling Tab
- Enable "Allow private key to be exported."
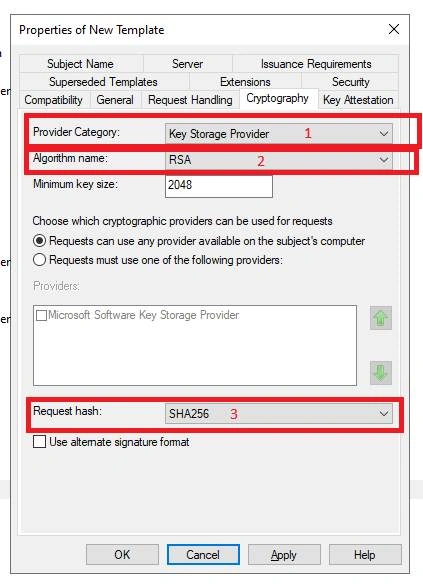
4. Cryptography Tab
- Provider Category: Key Storage Provider
- Algorithm Name: RSA
- Minimum Key Size: 2048
- Request Hash: SHA256
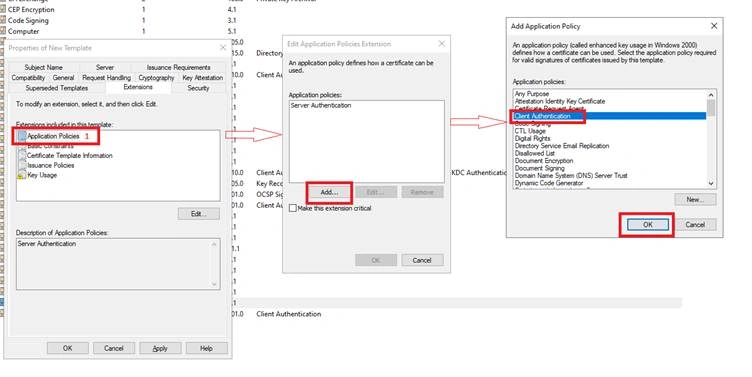
5. Extensions Tab
- Select Application Policies, click Edit, and add:
- Client Authentication
- Smart Card Logon (if required)
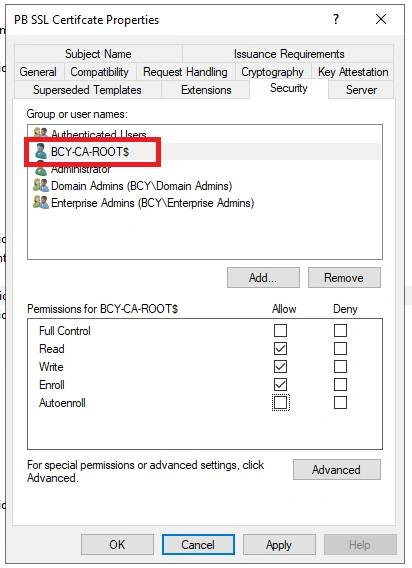
6. Security Tab
- Add specific users or groups if special permissions are needed beyond Domain Admins.
- Add the server names (including the application server) and assign the appropriate permissions. If the application servers are used to generate certificates, grant the necessary permissions to the CA server.
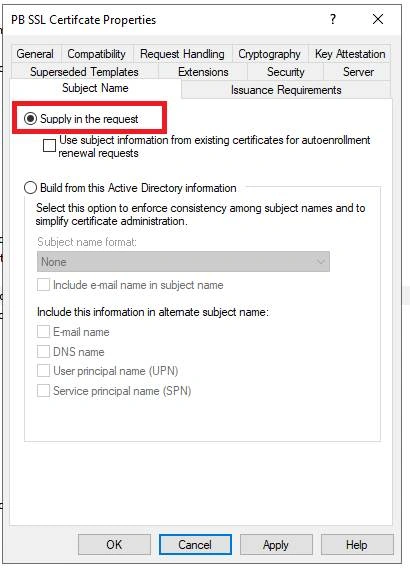
7. Subject Name Tab
- Select "Supply in the request."
8. Click Apply and then OK to save the template
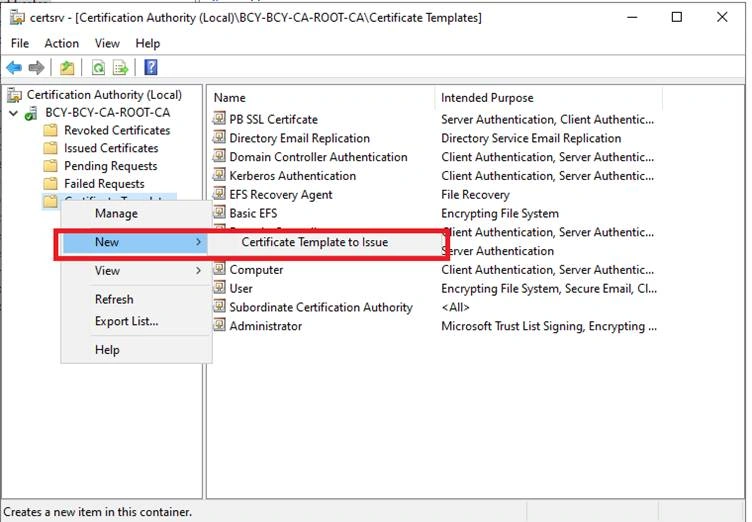
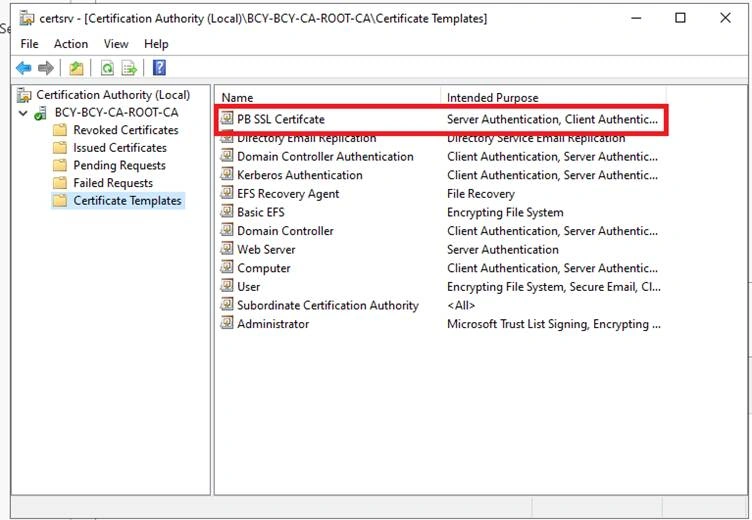
Step 2. Publish the New Template.
Join the conversation! Your thoughts help the community grow.