
Site to Site VPN (AWS to Azure)
AWS. Create VPC with 10.0.0.0/16, Public subnet 10.0.1.0/24. I need to create a Windows 2016 instance with a Public Subnet.
Azure. Create a Virtual network with 192.168.0.0/16, Public subnet 192.168.1.0/24. I need to create a Windows 2016 virtual machine with a Public Subnet.
I will provide a step-by-step guide to creating a Site-to-Site VPN (AWS to Azure) with screenshots below.
Go to AWS
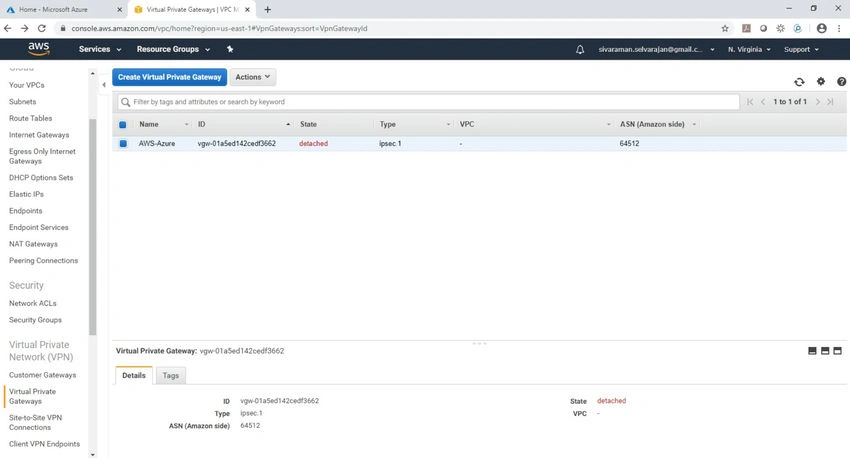
AWS (Amazon Web Services) Cloud to Create “VPC”, click “Virtual Private Gateways
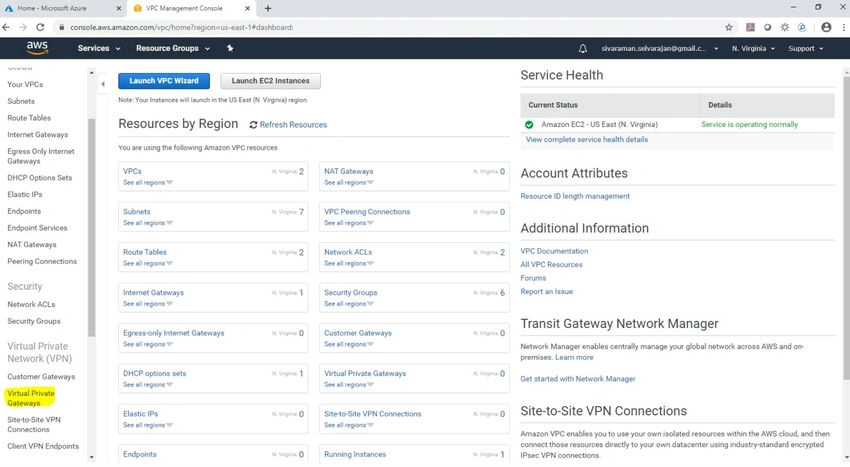
Next, Click “Create Virtual Private Gateway
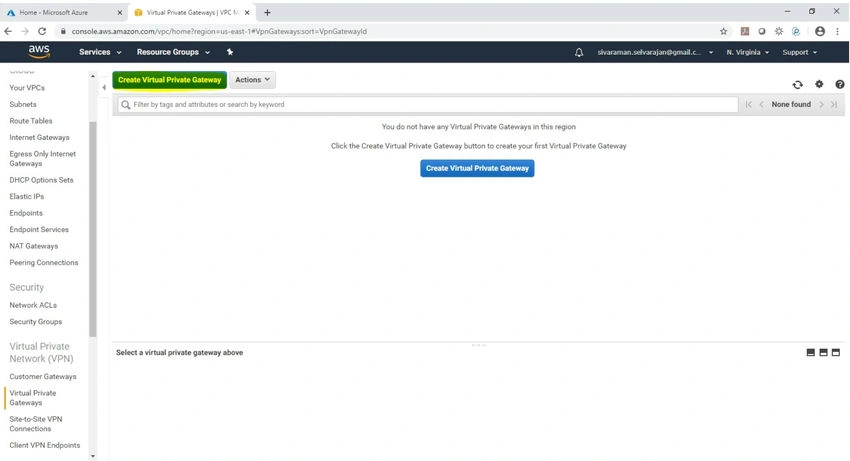
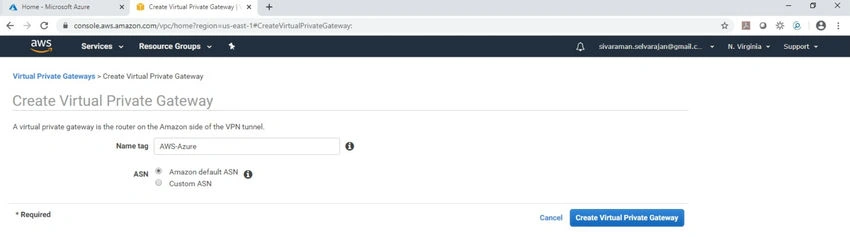
Type Name (Any Name)“AWS-Azure
Next, Click “Create Virtual Private Gateway
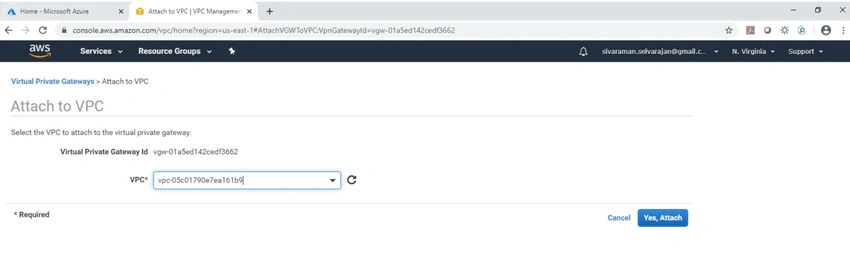
Select “AWS-Azure” -- > Actions Attach to VPC
Select “VPC” and click “Yes, Attach
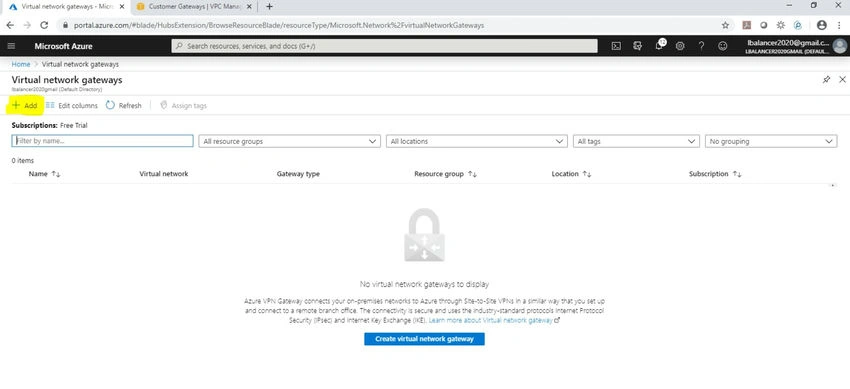
Go to Azure Next “Virtual network gateways. Click to “Add”
Next, Go to Gateway and type “VPN
Select the VPN Type “Route based"
Next, Select “virtual network” as “SANS-VNET
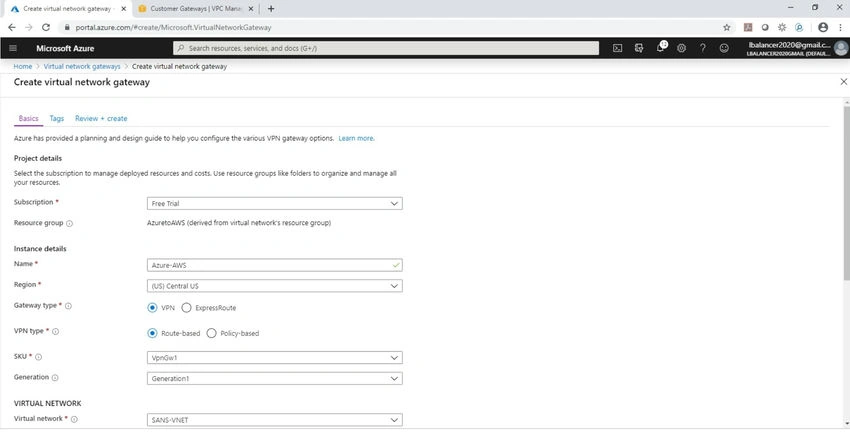
Public IP address name as “Azure-AWS. Click “Review + create
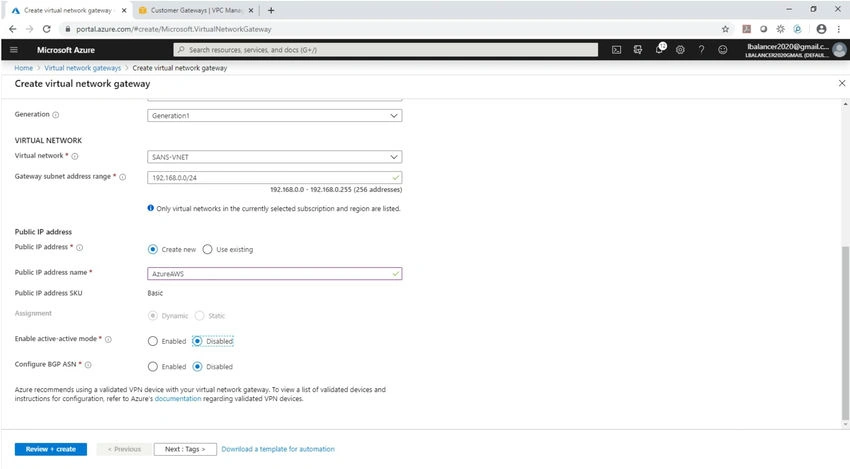
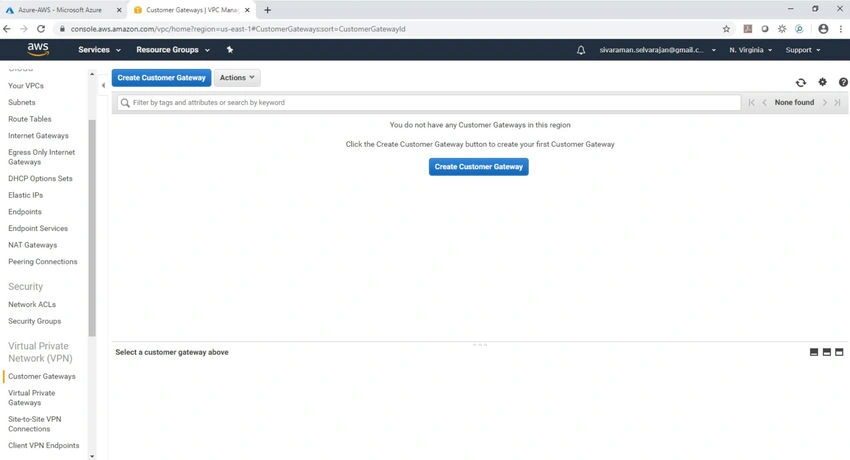
Next, Go to AWS In “Customer Gateway
Click “Create Customer Gateway”
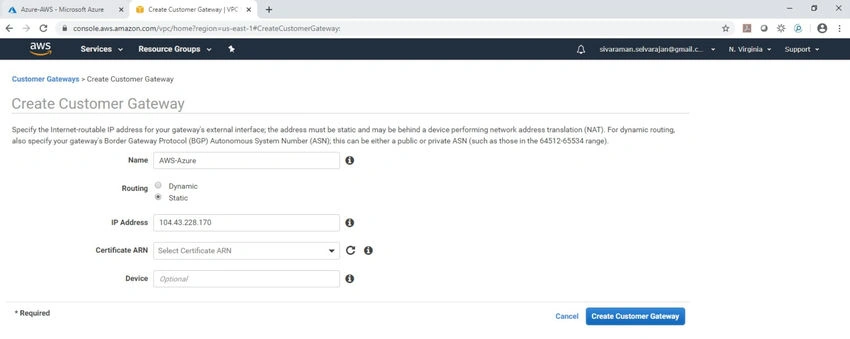
Type “Name” as “Aws-Azure”.
Routing “Static” as VPN gateway IP.
Click “Create Customer Gateway”
You have created a customer gateway.
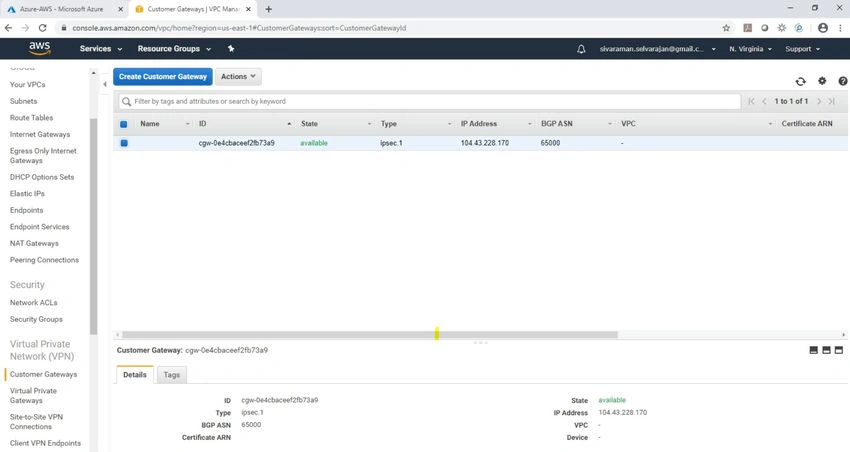
In “Site-to-Site VPN connections”,
Click “Create VPN connection.”
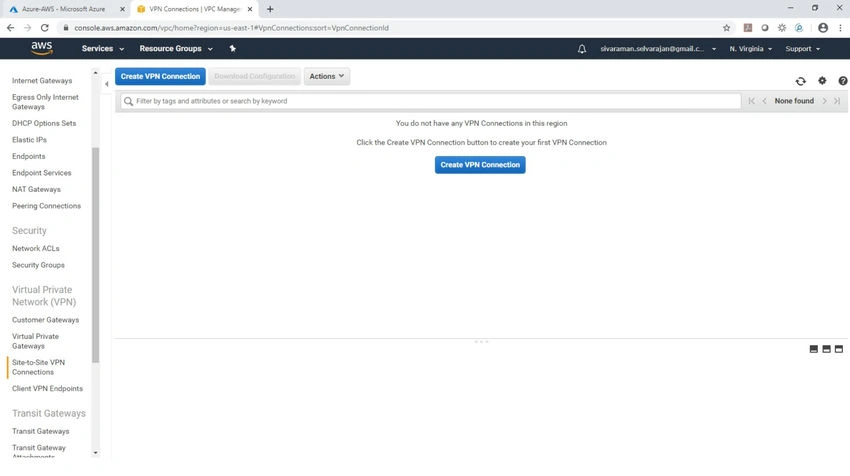
Name tag as “AWS-Azure”.
Target Gateway “Virtual Private Gateway”.
Select “Virtual Private Gateway” as select VPG.
Customer Gateway “Existing” and Customer Gateway ID select “CGW”.
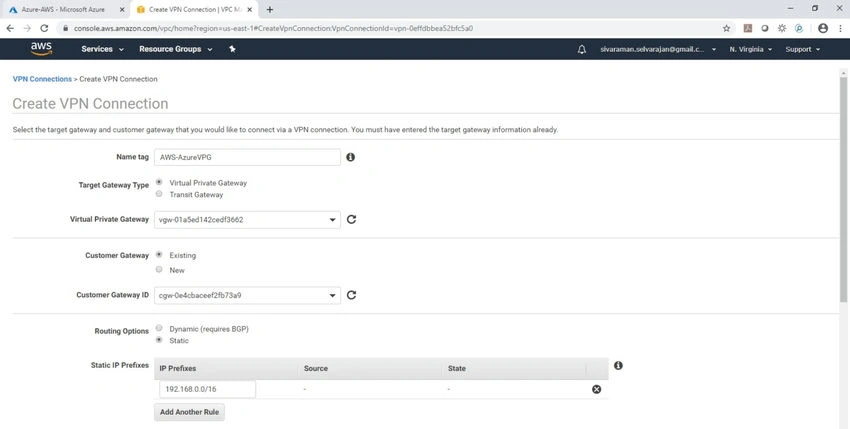
Click “Create a VPN connection
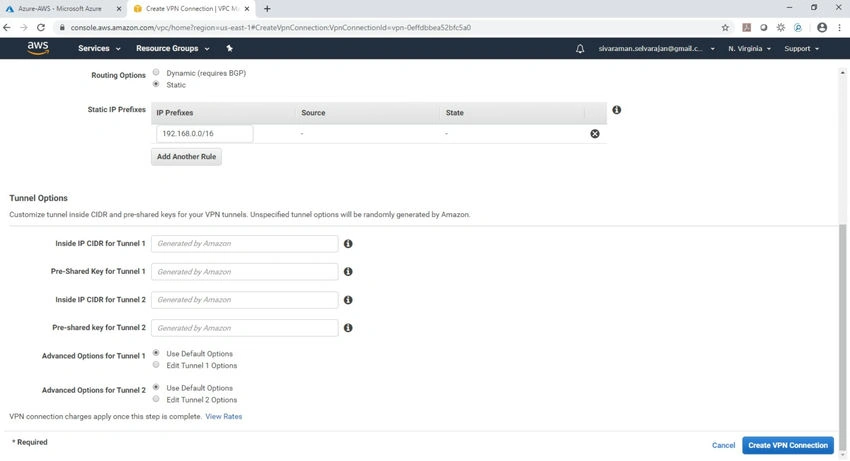
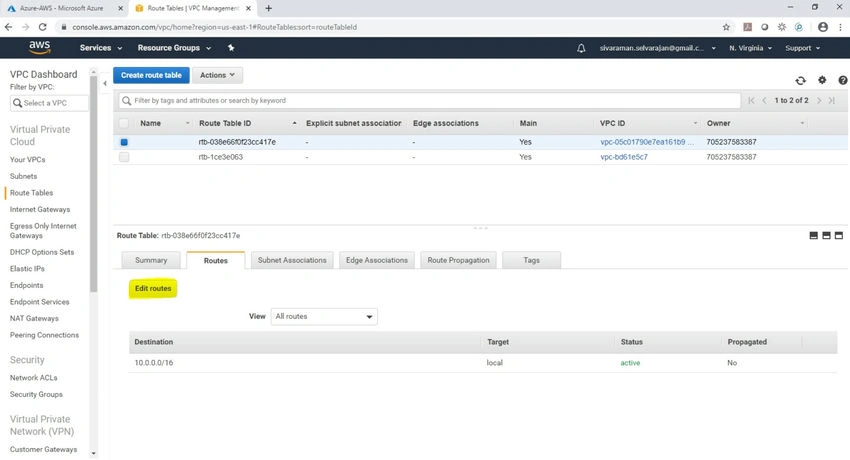
Next, Click “Route table
Click “Edit routes
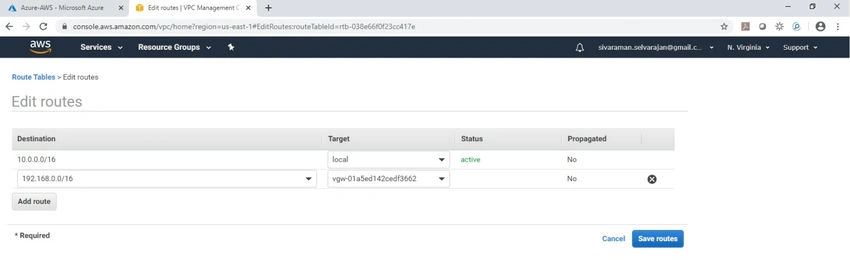
Type 192.168.0.0/16 subnet with Target as “Virtual Private Gateway
Click “Save route
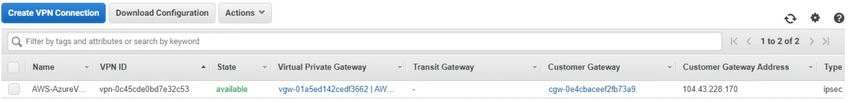
Please wait for some time it will become an available state.
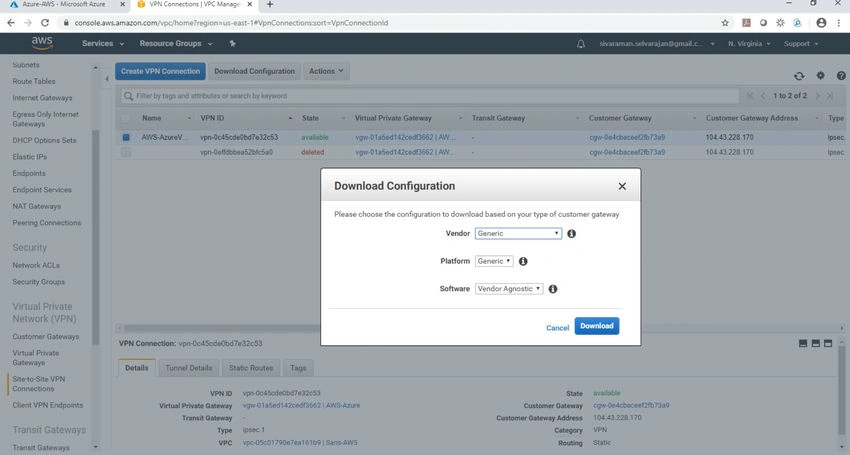
Select “Vendor” as Generic and Platform as “Generic” then click “Download.
Go to Azure. In “Local network gateways”, Click “Add
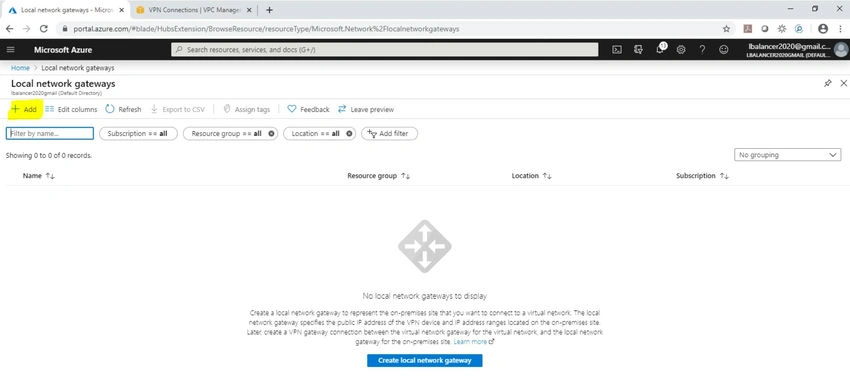
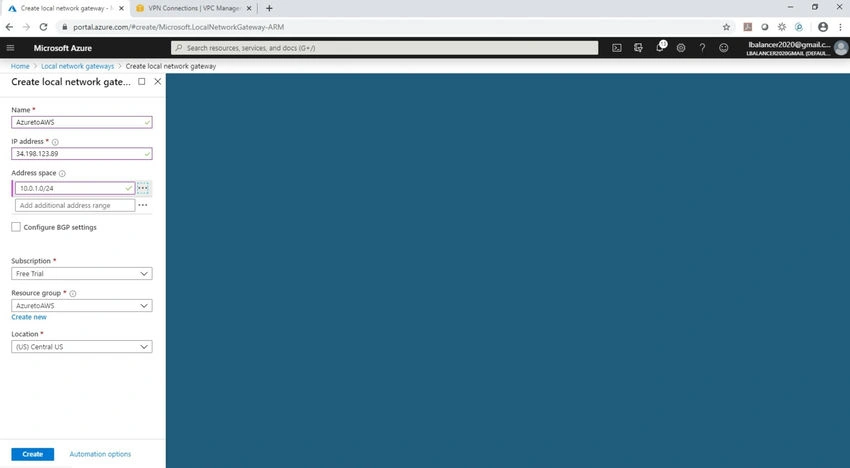
Type the Name as “AzuretoAWS”.
IP address as “VPG IP” address.
Address space as “10.0.0.0/16”. Click “Create”
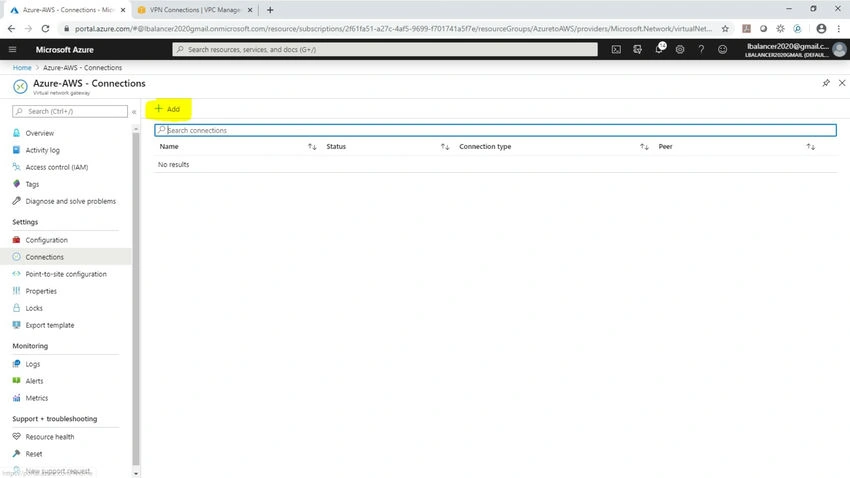
Click “Virtual network gateway.”
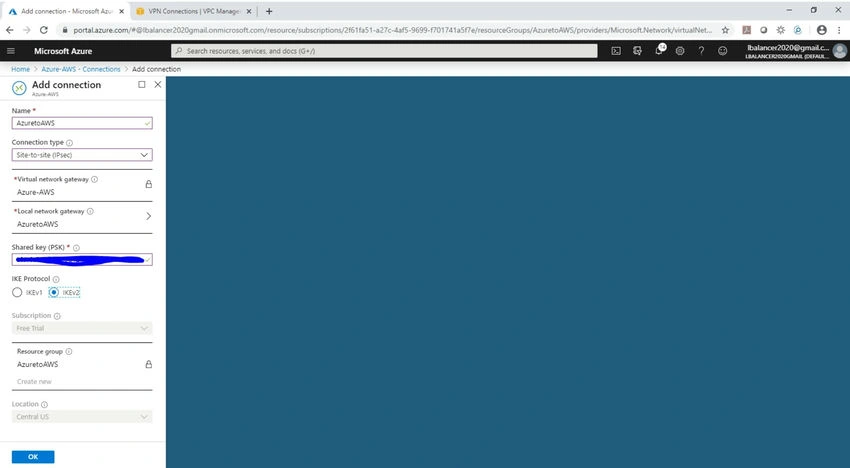
Type “Name” as “AzuretoAWS”.
Connection type “Site-to-Site” Select “Local network gateway”.
Type “Preshared key” from the Downloaded configuration file (AWS).
IKE protocol IKEv2. Click “Ok”
Now, the status become Connected.
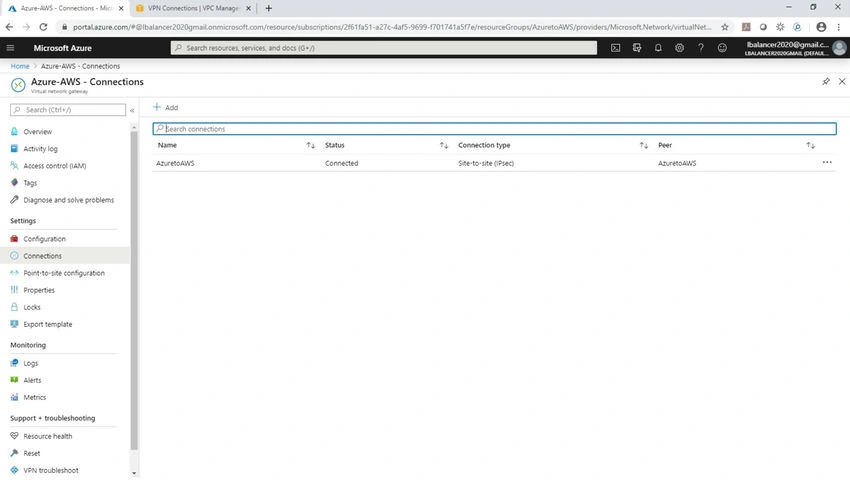
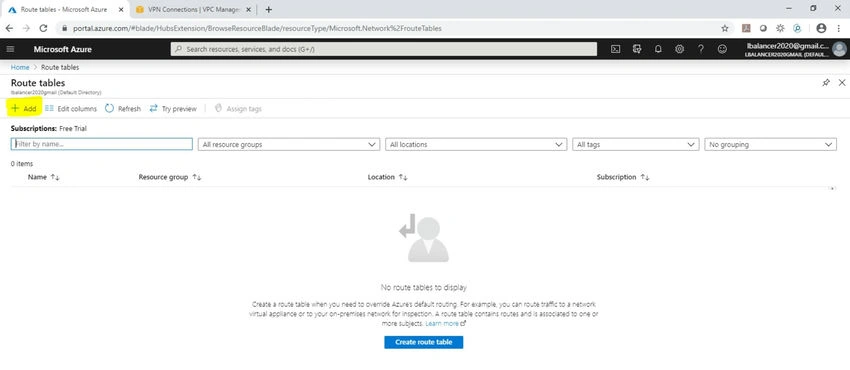
Go to Route table, Click “Add
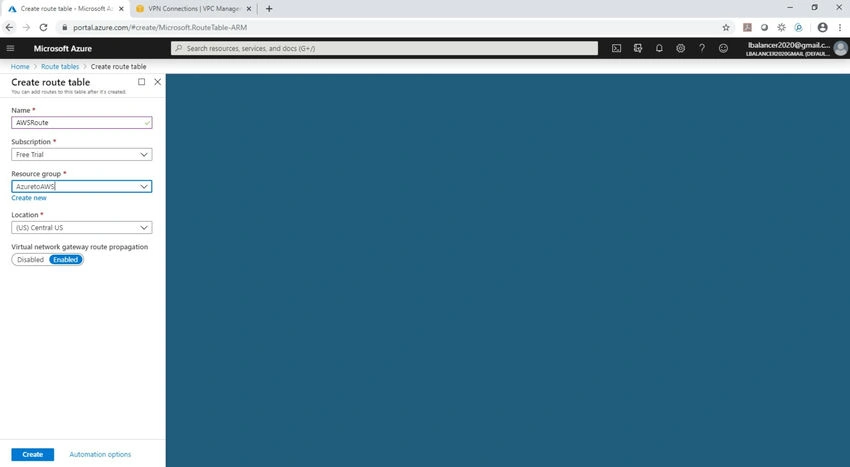
While creating the route table, Type “Name” as “AWSRoute”.
Subscription as “Free Trial”.
Select “Resource group” as “AzuretoAWS”.
Location “Central US”.
Virtual network gateway route propagation Enabled. Click “Create”
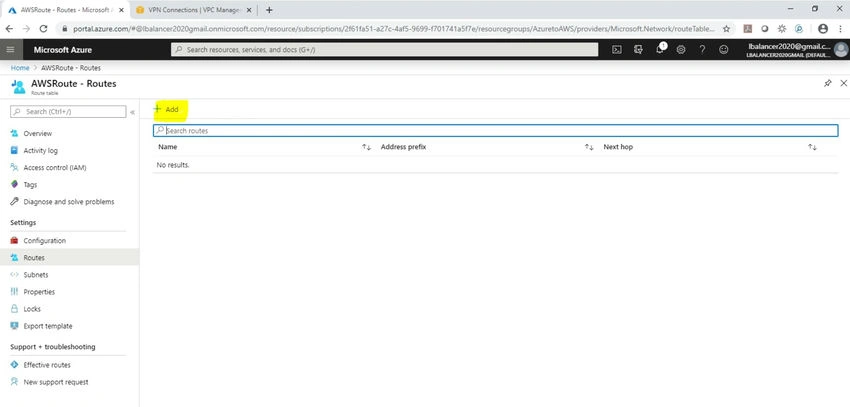
In “Routes”, Click “Add”
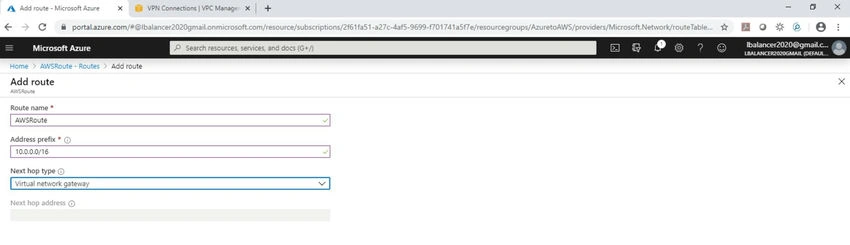
While “Add Route”,
Type “Route name” as “AWSRoute”.
Type the Address prefix as 10.0.0.0/16. Select “Next hop type” as “Virtual network gateway”. Click “Ok”
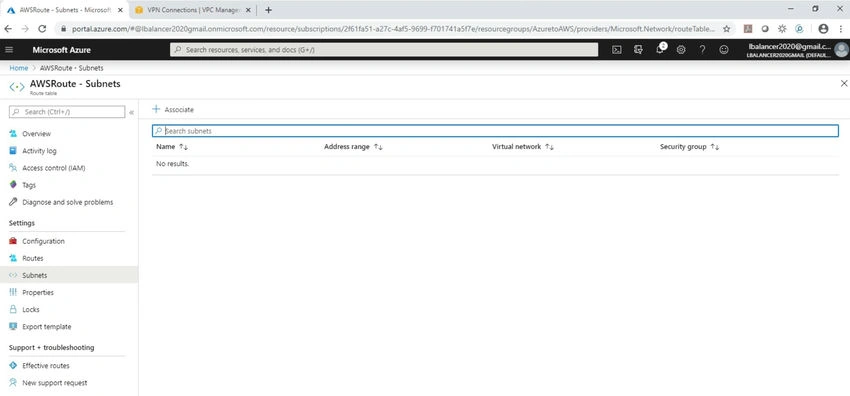
In “Subnets”, Click “Associate.
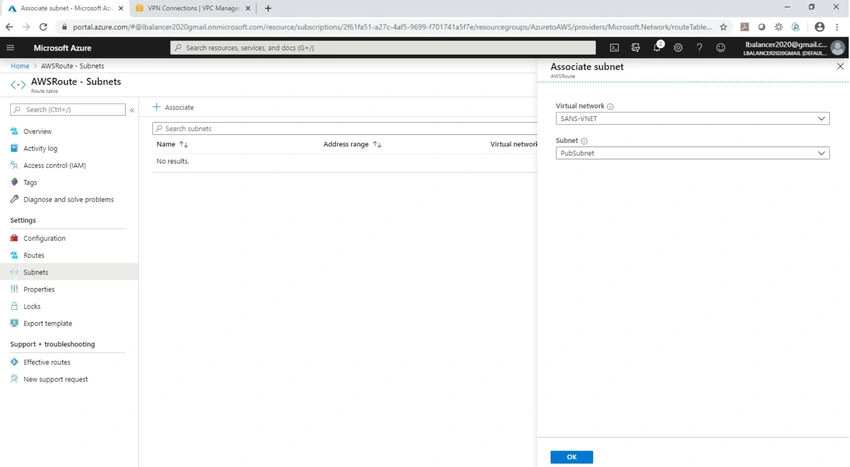
While “Associate subnet”,
Select “Virtual network” as “SANS-VNET”.
Select “Subnet” as “PubSubnet”.
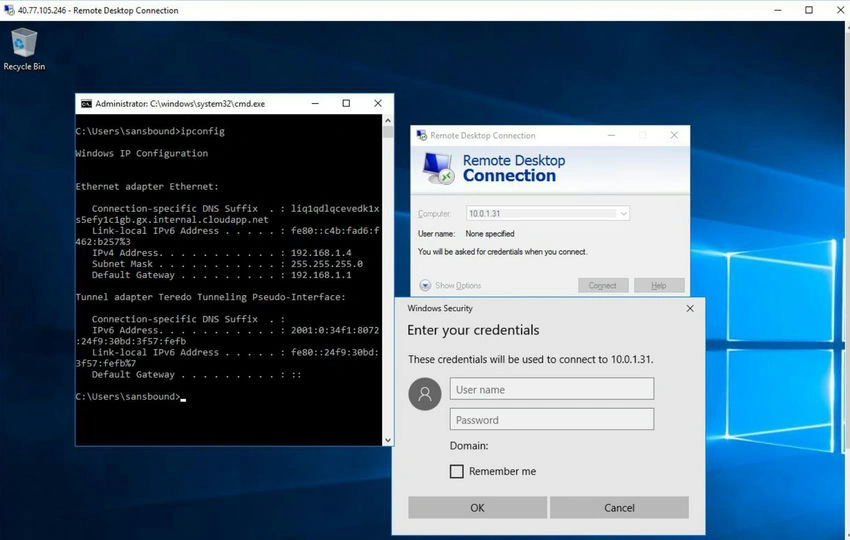
We have successfully connected the AWS instance from Azure.
Conclusion
This article taught us how to create a Site-to-Site VPN (AWS to Azure). If you have any questions, please contact me.
Thanks.
Join the conversation! Your thoughts help the community grow.