

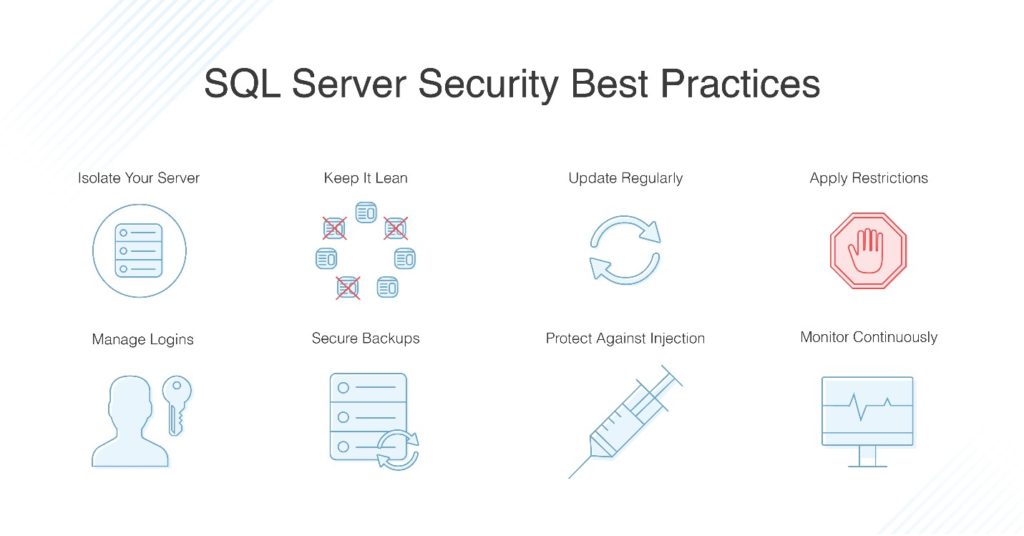
Security is one of the most important aspects of any database system.
As developers, we often focus on performance and forget that a single insecure query or open permission can expose sensitive business data.
In this article, let’s understand SQL Server Security Best Practices that every developer should follow — with examples, explanations, and a simple flowchart.
🔐 Why Security Matters
Modern applications store critical data — user credentials, financial transactions, personal information, etc.
If your SQL Server isn’t configured securely, attackers can exploit vulnerabilities such as:
SQL Injection
Privilege Escalation
Data Leakage
Unauthorized Access
That’s why database-level security must be a shared responsibility between developers and DBAs.
🧩 Security Layers in SQL Server
Before jumping into best practices, understand that SQL Server security has multiple layers :
Authentication: Who can access the server
Authorization: What actions they can perform
Encryption: How data is protected in transit and at rest
Auditing: Tracking who did what and when
⚙️ Best Practices for Developers
Let’s break down the most essential security best practices step by step.
1. Use Parameterized Queries (Prevent SQL Injection)
Never concatenate user input directly in your SQL statements.
❌ Vulnerable Example
string query = "SELECT * FROM Users WHERE Username = '" + userInput + "'";
✅ Safe Example
    SqlCommand cmd = new SqlCommand("SELECT * FROM Users WHERE Username = @Username", conn);
cmd.Parameters.AddWithValue("@Username", userInput);
Why: Parameterized queries ensure that input is treated as data, not executable SQL, preventing SQL injection attacks.
2. Follow the Principle of Least Privilege
Grant only the permissions required — nothing more.
❌ Don’t
Use
saor system admin accounts for applications.Give
db_ownerrole to every user.
✅ Do
Create application-specific users with limited access.
Assign roles like
db_datareaderordb_datawriteras needed.
3. Secure Connection Strings
Never store connection strings in plain text inside your source code.
✅ Use Configuration Files or Secrets Manager:
.NET Core: Store in
appsettings.jsonand protect with User Secrets or Azure Key Vault.Windows: Use DPAPI or Encrypted Configuration Sections.
Example
    "ConnectionStrings": {
  "DefaultConnection": "Server=myServer;Database=myDB;User Id=appUser;Password=***;"
}
4. Encrypt Sensitive Data
Use SQL Server encryption features to protect confidential data.
🔸 Transparent Data Encryption (TDE)
Encrypts the database files (.mdf, .ldf) at rest.
    CREATE DATABASE ENCRYPTION KEY
WITH ALGORITHM = AES_256
ENCRYPTION BY SERVER CERTIFICATE MyServerCert;
ALTER DATABASE MyDB SET ENCRYPTION ON;
🔸 Column-Level Encryption
Encrypt specific columns like passwords or credit card numbers.
    CREATE COLUMN MASTER KEY MyKey
WITH ALGORITHM = RSA_2048;
5. Avoid Hardcoding Credentials
❌ Never hardcode usernames, passwords, or keys in your code.
✅ Always use:
Environment variables
Secure configuration management
Secret stores (e.g., Azure Key Vault, AWS Secrets Manager)
6. Enable Row-Level Security (RLS)
Row-Level Security restricts data visibility based on user or role.
Example
    CREATE SECURITY POLICY SalesFilter
ADD FILTER PREDICATE dbo.fnSecurityPredicate(UserID)
ON dbo.Sales WITH (STATE = ON);
Join the conversation! Your thoughts help the community grow.