
The Azure connections in the Microsoft Fabric Admin Portal are an important feature that allows connecting Azure services to Fabric which enables seamless integration and data management. Specifically, the Azure connections allow businesses to store dataflows in their organization’s Azure Data Lake Storage Gen2 (ADLS Gen2) account.
The following are some of the key benefits.
- Tenant-level storage: allows storing dataflows in the organization’s tenant settings which can serve as a central Data Lake storage location or as a default storage place in addition to workspace-level storage.
- Workspace-level storage permissions: By default, workspace admins cannot connect their own storage accounts. However, Fabric administrators can enable a setting that allows workspace admins to connect their own storage account ensuring flexibility that enhances data management within specific ADLS Gen2 accounts, organized based on workspace.
Granting Ownership Permission in Azure Storage Account IAM
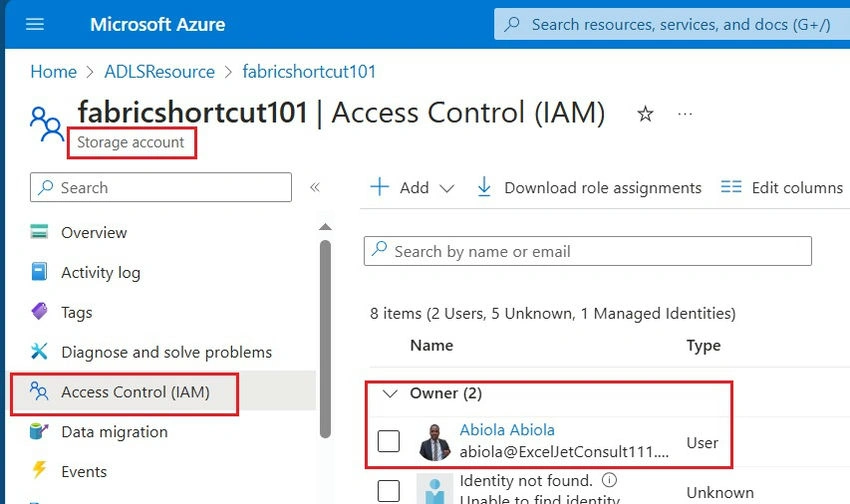
To successfully connect the ADLS Gen2 account in the Microsoft Fabric Admin Portal, it is mandatory to have Owner permission at the storage account layer. Permissions at the resource group or subscription level won't work and if you're an administrator, you must assign yourself the Owner permission. To grant ownership permission.
- In the Storage Account of the Azure Portal, select Access Control (IAM).
- At the top, click on +Add and select Add role assignment.
- Select the Privileged Administrator Roles tab.
- Click on Owner.
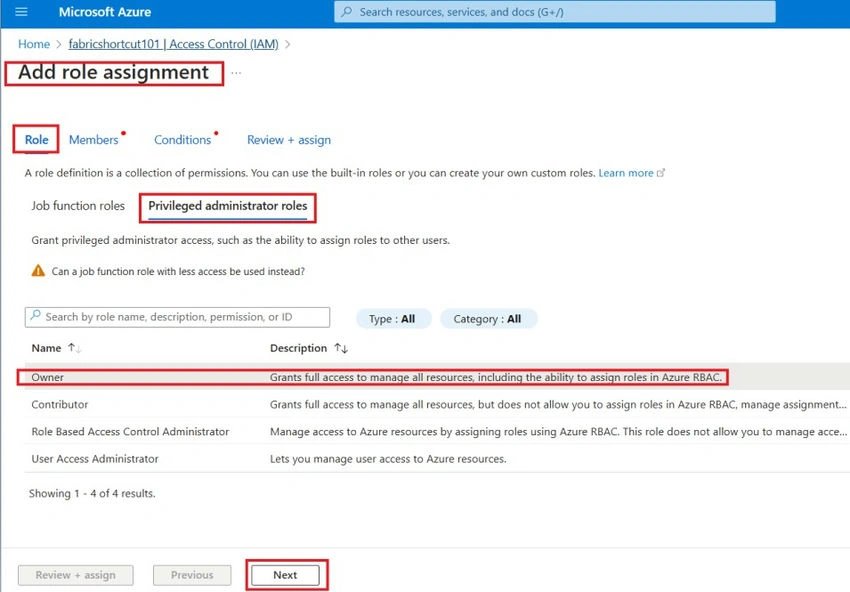
- Select Next,
- In the Members tab, click on Select Members and choose the member to add. In my case, I added myself as a member as seen in the screenshot below.
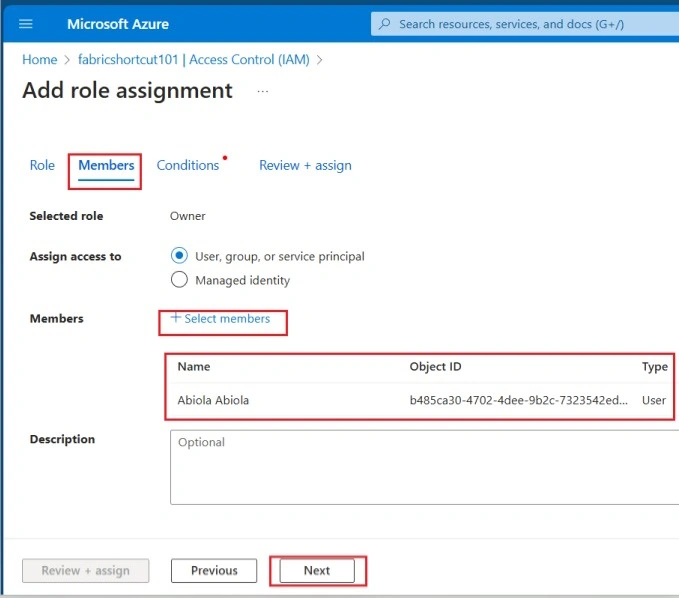
- Click Next,
- In the Conditions tab, select Allow user to be assigned all roles except privileged administrator roles Owner, UAA, RBAC.
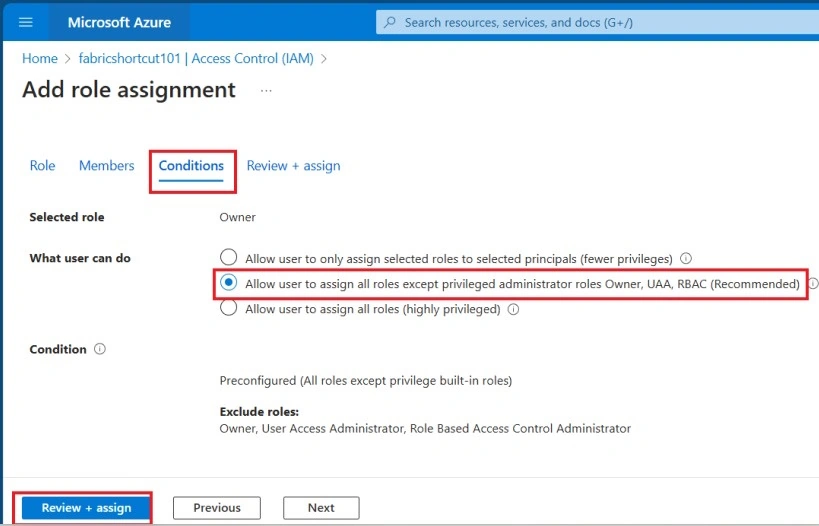
- Click Review + Assign.
- In the screenshot below, I can see Abiola Abiola as Owner. This is sorted in the Azure Portal.
Connecting to the Azure Resources in the Fabric Admin Portal
After establishing the ownership permission in the Azure Portal, we're going to shift focus on Azure Resources tenant-level storage in the Microsoft Fabric Admin Portal.
- In the Fabric Admin Portal, locate Azure connections.
- Click on the Tenant-level storage expand icon.
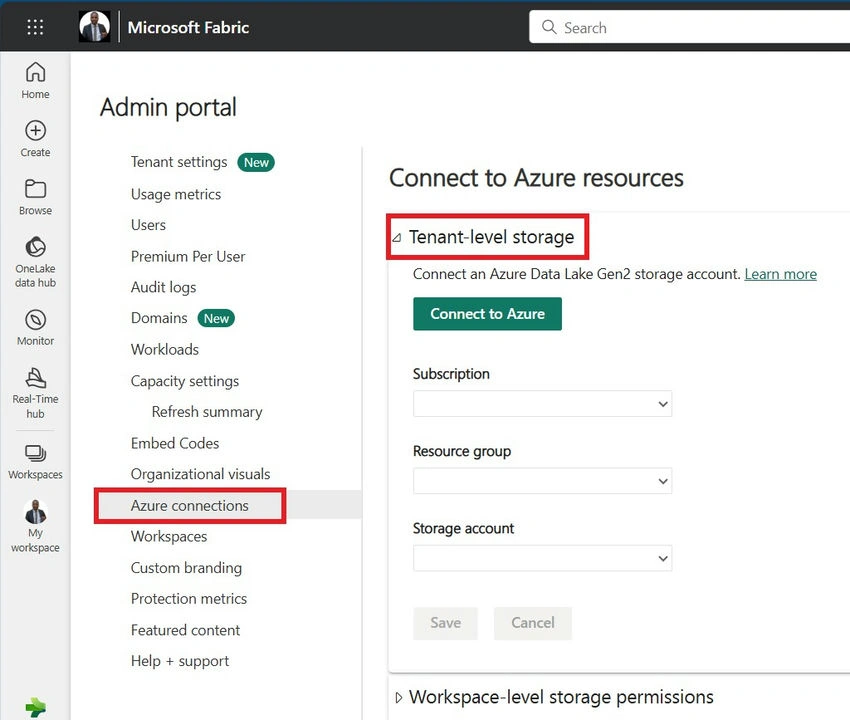
- Click on the Connect to Azure.
- Select the Azure Subscription from the Subscription dropdown.
- Select the Resource group from the Resource group dropdown.
- Select Storage account from the Storage account dropdown.
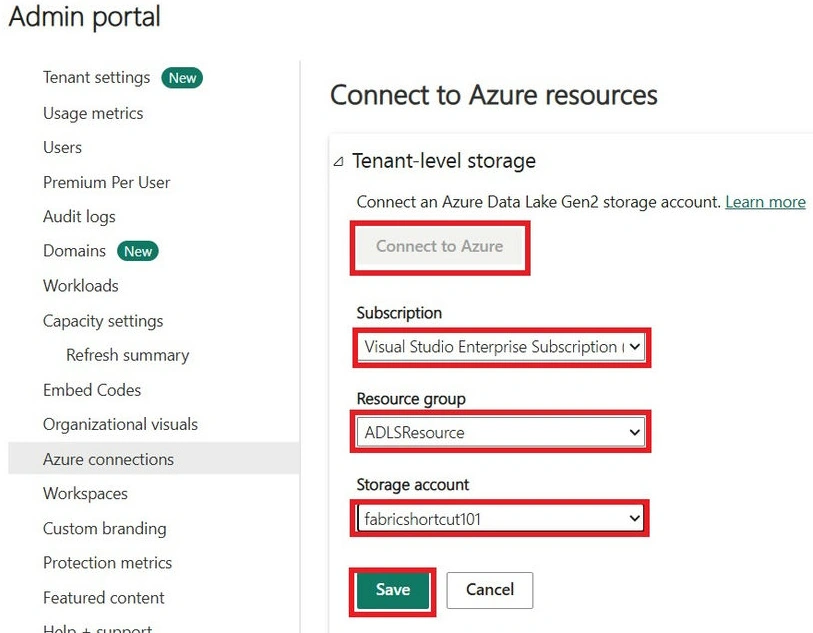
- Click Save.
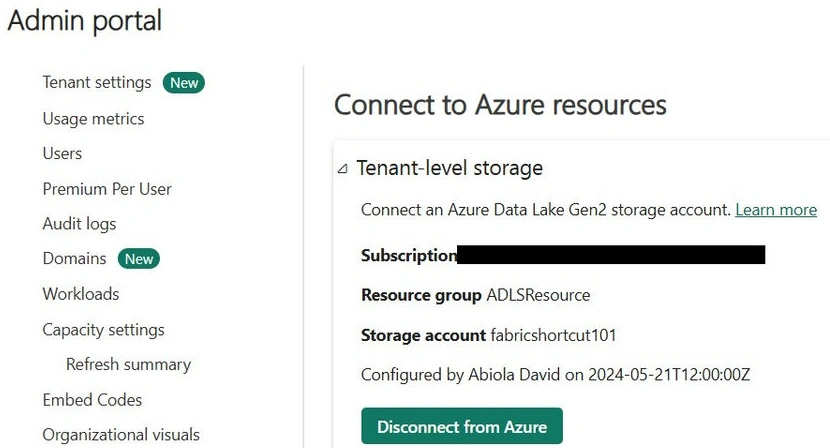
- In the screenshot below, the connection has been established to Azure and we have details such as Subscription, Resource group, and Storage account names including the name of the configurator, date, and time.
Join the conversation! Your thoughts help the community grow.