
We found ourself in a situation where we need to authenticate azure, Call Azure REST API when we are working with Azure. Applications like PowerShell scripts and .NET, JAVA or any other application need to authenticate azure in order to perform actions in azure. In order to call the REST API, we have to use an authentication token.
In this post, I will describe the following areas.
- Create Service Principal
- Generate Authtoken using Postman REST API call
- Generate AuthToken using Powershell
Create Service principle
What is Service Principal?
Service principles are non-interactive Azure accounts. Applications use Azure services should always have restricted permissions. Azure offers Service principals allow applications to login with restricted permission Instead of having full privilege in a non-interactive way.
Using Service Principal we can control which resources can be accessed.
For security reason, it’s always recommended to use service principal with automated tools rather than allowing them to log in with user identity
Create a Service Principal with PowerShell.
Note
For this demo we are using Azure RM PowerShell module
For this demo we are using Azure RM PowerShell module
Create AD app
- #Create AD app
- $dummyUrl = "https://dummy.dummy.com"
- $passpowrd = "Qwerty@123!"
- $securePassword = ConvertTo-SecureString -String $passpowrd -AsPlainText -Force
- $app = New-AzureRmADApplication -DisplayName $dummyUrl `
- -IdentifierUris $dummyUrl `
- -HomePage $dummyUrl `
- -Password $securePassword -Verbose
- Create a Service Principal
- #Create Service principal
- New-AzureRmADServicePrincipal -ApplicationId $app.ApplicationId `
- -DisplayName $dummyUrl `
- -Password $securePassword `
- -Scope "/subscriptions/<SUBSCRIPTION ID>" `
- -Role Contributor `
- -StartDate ([datetime]::Now) `
- -EndDate $([datetime]::now.AddYears(1)) -Verbose
This service principal is valid for one year from the created date and it has Contributor Role assigned. Further using this Service principal application can access resource under given subscription. We can scope to resources as we wish by passing resource id as a parameter for Scope.
View created AD app in Portal
- Log in Portal
- Go to Azure Active Directory -> App Registrations
- We can find the created app as below,
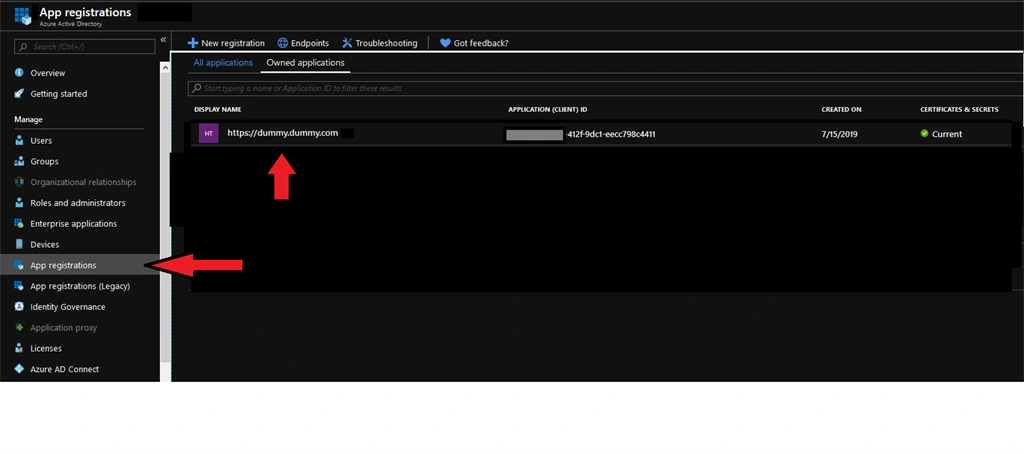
- Once we click the app we will see app details as below,
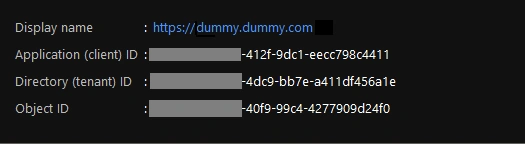
Keep these records as we need later.
Get Auth token by calling Rest API in Postman
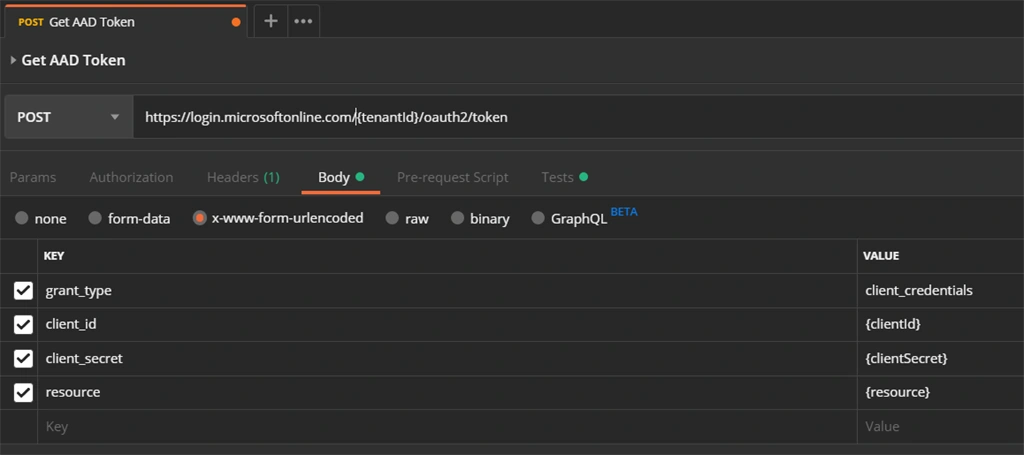
- Create a new Post Request
- Create New POST request in Postman
- Update Url as below
https://login.microsoftonline.com/{TENANTID}/oauth2/token
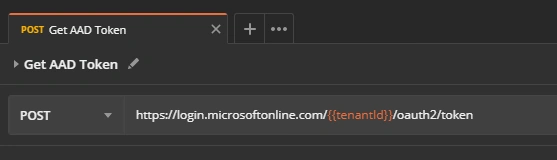
Replace {TENANTID} with tenantId we got when we create service principle.
Set the Request Body,
Select x-www-form-urlencoded radio,
Add following parameters,
| Parameter Name | Value |
| grant_type | client_credentials |
| client_id | APPLICATION / CLIENT ID WE GOT WHEN WE CREATE SERVICE PRINCIPLE |
| client_secret | PASSWORD WE USED WHEN CREATING SERVICE PRINCIPLE IN ABOVE |
| resource | https://management.azure.com/ |
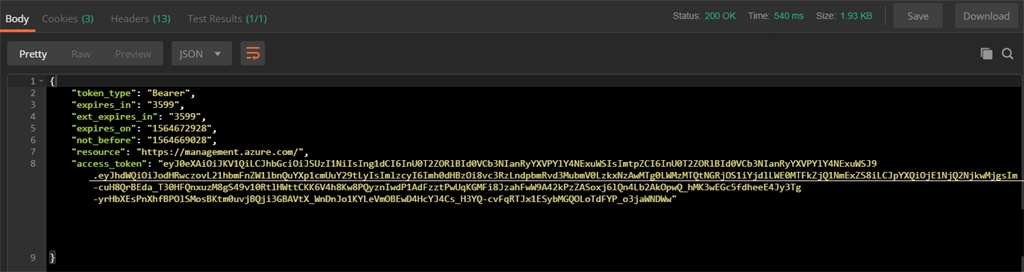
Send the request and observe the result. You will receive output like below.
Ajay JaiswalPosted Jul 17, 2020, 4:08 AM
I'm writing java code to connect AzureSqlServer using token but after an hour the access token gets expire.
Ajay JaiswalPosted Jul 17, 2020, 4:06 AM
How to get refresh token as it gets expire in an hour.