
Introduction
JSON Web Token is an open industry standard RFC7516 method for representing claims between two parties that we will look at in this blog. JSON Web Token is an open standard that allows data to be transmitted between parties as a JSON file that is securely signed and trusted. JWT Token Authentication is widely popular in Website Development. JWT Token Authentication can be signed using a secret (with HMAC Algorithm) or with public or private key pairs using RSA or ECDSA.
JSON Web Token can be encrypted and provide secrecy between the parties. We will focus on signed tokens to verify the claims contained with It. JSON Web Token looks like this

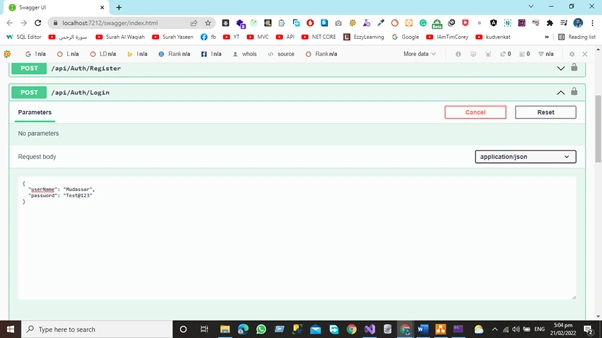
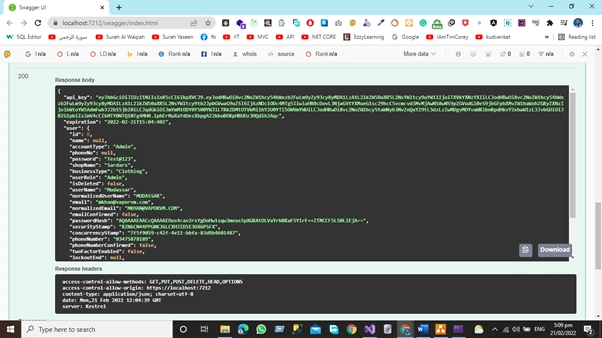
JSON Web Token Example from Real-World Project
In my next article code for this project will be available
"eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJodHRwOi8vc2NoZW1hcy54bWxzb2FwLm9yZy93cy8yMDA1LzA1L2lkZW50aXR5L2NsYWltcy9uYW1lIjoiTXVkYXNzYXIiLCJodHRwOi8vc2NoZW1hcy54bWxzb2FwLm9yZy93cy8yMDA1LzA1L2lkZW50aXR5L2NsYWltcy9tb2JpbGVwaG9uZSI6IjAzNDc1ODc4MTg5IiwiaHR0cDovL3NjaGVtYXMueG1sc29hcC5vcmcvd3MvMjAwNS8wNS9pZGVudGl0eS9jbGFpbXMvZW1haWxhZGRyZXNzIjoibWtoYW5AdmFwb3J2bS5jb20iLCJqdGkiOiJiZTc4YmY1OC0wZDg3LTRjZWUtYTJmNC0xOGM3ZjVmZmU2NGQiLCJodHRwOi8vc2NoZW1hcy5taWNyb3NvZnQuY29tL3dzLzIwMDgvMDYvaWRlbnRpdHkvY2xhaW1zL3JvbGUiOiJBZG1pbiIsImV4cCI6MTY0NTQ0MTI2MX0.17WuapLSXYLiMGErZB1dtmBFKz5xuJvxTWQsSS57GLk",
But if want to see what is inside this JSON Web Token we first go to jwt.io
Follow the link above and Decode this Token and we will see what is inside this token
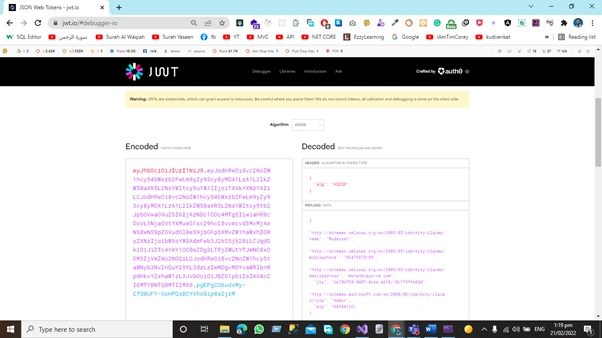
Copy your JSON Web Token and go the jwt.io and open the debugger tab

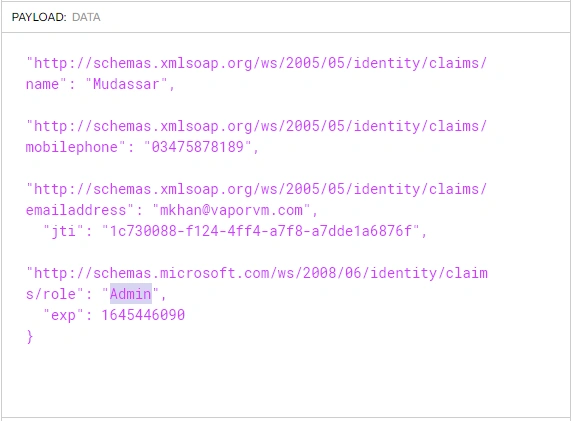
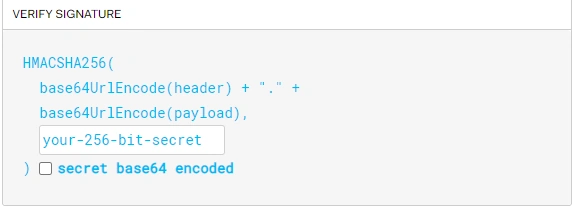
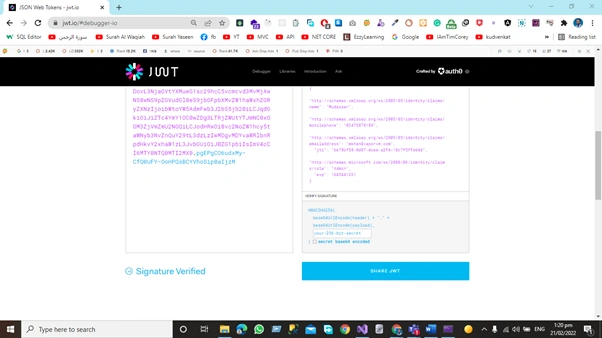
Copy and paste the JWT Token Code into the Encoded Tab. When we paste the code in the encoding tab, our Decoded JWT Token is on the right side, with the Header, Payload, and Verify Signature, as seen in the image below.
Header
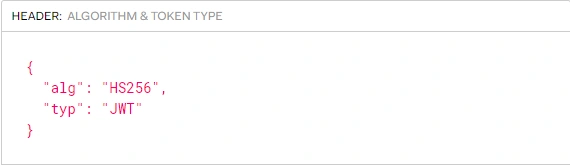
The header is the combination of two parts. The first part of the token is the
- Signing Algorithm HMAC 256, 512
- Type of the Token
Example
Join the conversation! Your thoughts help the community grow.