
Introduction
Security tokens are becoming a standard way of applying security to web apis. Applying token based authentication is fairly easy method as client just need to send security token with every request is made to server.
You can view entire source code on Github from here
Software’s needed
- Node JS - Platform
- Postman – used for creating http requests like GET, PUT, POST, DELETE
- Sublime/Notepad++ - IDE for writing code.
Installing dependencies
We will be using jsonwebtoken npm package for creating web token and for verifying the same for the subsequent requests.
- Npm install express sequelize body-parser jsonwebtoken morgan
- var express = require('express'),
- bodyParser = require('body-parser');
- var users = require('./users.json');
- var logger = require('morgan');
- var app = express();
- app.use(bodyParser());
- app.use(logger('dev'));
- var port = 8080; //setting port no.
- var jwt = require('jsonwebtoken');
- app.set('superSecret', "success is inevitable");
- var router = express.Router();
- router.post('/authenticate', function(req, res) { //this will issue token for valid users
- var username = req.body.user;
- var password = req.body.password;
- var isUserFound = false;
- var foundUser = {};
- console.log(req.body.user + " " + req.body.password);
- for (var i = 0; i < users.length; i++) {
- if (users[i].user === req.body.user) {
- isUserFound = true;
- foundUser = users[i];
- }
- }
- if (isUserFound) {
- if (foundUser.password == req.body.password) {
- var token = jwt.sign(foundUser, app.get('superSecret'), {
- expiresInMinutes: 1440 // expires in 24 hours
- });
- console.log(token);
- res.json({
- success: true,
- message: 'Enjoy your token!',
- token: token
- });
- } else {
- res.json({
- success: false,
- message: 'Authentication failed. Wrong password.'
- });
- }
- res.send(foundUser);
- } else {
- res.json({
- success: false,
- message: 'Authentication failed. user not found.'
- });
- }
- });
- [{
- "user": "[email protected]",
- "password": "test"
- }, {
- "user": "[email protected]",
- "password": "vijay"
- }]
- //middleware
- router.use(function(req, res, next) {
- // check header or url parameters or post parameters for token
- var token = req.body.token || req.query.token || req.headers['x-access-token'];
- // decode token
- if (token) {
- // verifies secret and checks exp
- jwt.verify(token, app.get('superSecret'), function(err, decoded) {
- if (err) {
- return res.json({
- success: false,
- message: 'Failed to authenticate token.'
- });
- } else {
- // if everything is good, save to request for use in other routes
- req.decoded = decoded;
- next();
- }
- });
- } else {
- // if there is no token
- // return an error
- return res.status(403).send({
- success: false,
- message: 'No token provided.'
- });
- }
- });
- router.get('/users', function(req, res) {
- //console.log(User);
- return res.json({
- status: 'OK',
- msg: "you are authenticated and all set to consume our services."
- });
- });
- router.use(function(req, res, next) {
- // do logging
- console.log('Something is happening.');
- next();
- });
- app.use('/api', router);
- // START THE SERVER
- // =============================================================================
- app.listen(port);
- console.log('Magic happens on port ' + port);
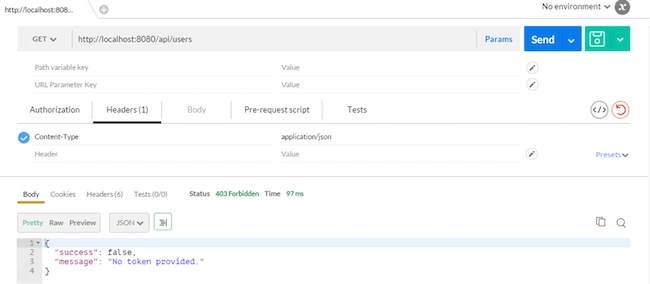
2. We are sending valid user to fetch token at /api/authenticate.
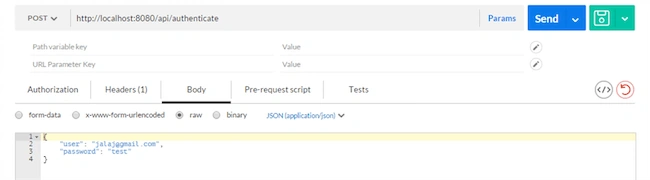
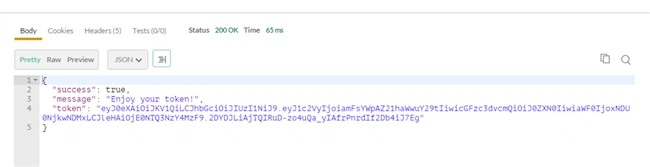
Response http msg
david johnPosted Jul 6, 2019, 1:14 AM
Thanks for sharing this useful info. I also want to share some info about the Node JS Training Institute in Munirka which will surely increase your knowledge regarding various concepts of Node JS learning that help you in preparation for easily getting a job in a good company. For more details, visit: https://www.dtacademy.in/
katheeja beeviPosted Nov 24, 2018, 12:57 AM
How to validate with oracle?