
Introduction
AWS Identity and Access Management (IAM) is one of the AWS services that helps you securely control AWS resources. Any organization has different resources for different services, so IAM controls who is authenticated and authorized (permission) to use these resources. When you first start on AWS, you begin with a single sign-in identity who has complete access to all AWS services and resources. This identity is called the AWS root user and can be accessed via the credentials you used while creating the AWS account.
After creating the AWS root account, the next step is to start working with the services of AWS. Before this, it is strongly recommended that you do not use the AWS root account even for Administrative tasks. To begin, for any further services use an IAM user and only use the root account to create an IAM user.
IAM Features
Granular Permissions
You can grant different permissions to different people for different resources.
E.g., you allow a user complete access to Amazon EC2, Amazon S3, and dynamo DB for other users you allow only read access to amazon EC2 only nothing else so these users access resources according to their permissions.
Secure access to AWS resource
IAM credentials provide secure access for your application to access other AWS resources
eg. S3 buckets, dynamo DB
Multi-factor Authentication (MFA)
You can add multi-factor authentication to your account for extra security
E.g., along with a password, you additionally provide a code from a configured device.
IAM main resources
- IAM users
- IAM groups
- IAM roles
- IAM policies
IAM users are usually a physical person like you or me. It usually represents a person or service who uses it to interact with AWS
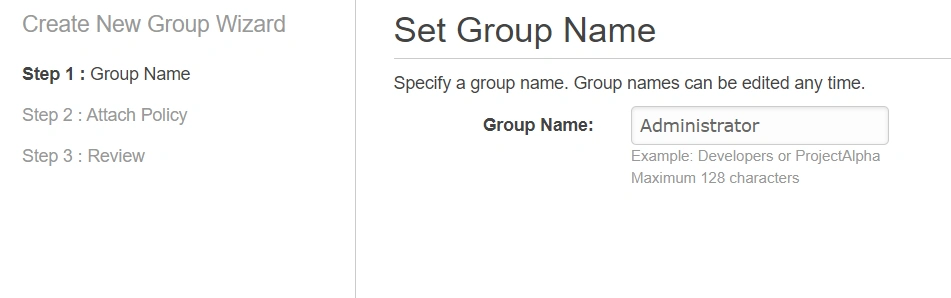
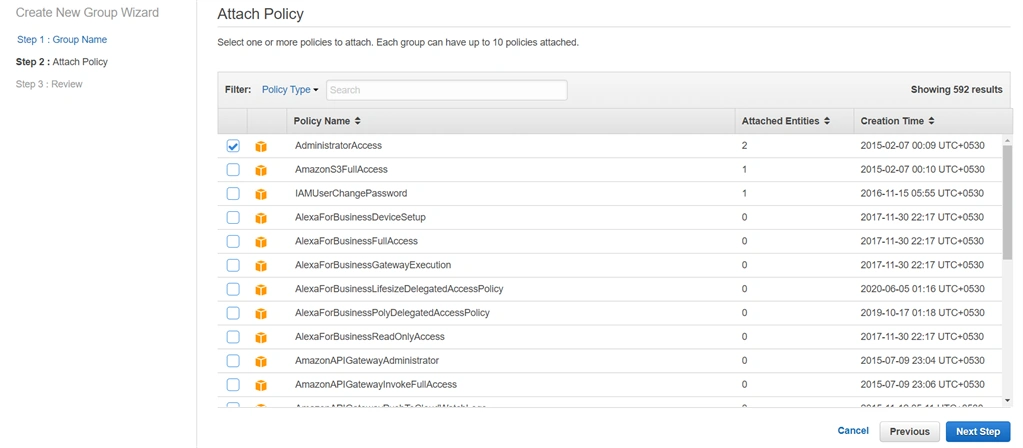
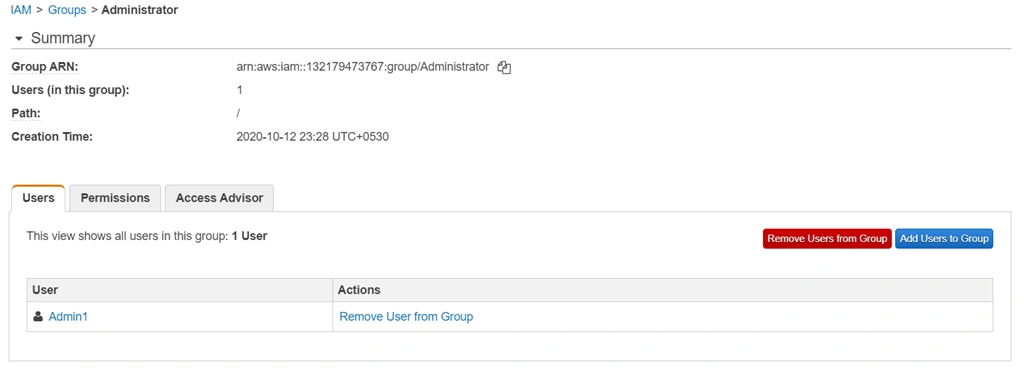
Now users can be grouped together IAM Groups which use to specify permissions for a collection of users, suppose you have a group called admins, and give that types of permissions that administrators typically need. any user in that group automatically has the permissions that are assigned to the group now if a new user joins organizations and should have administrator privilege you can assign these permissions by adding the user to that group.
IAM roles are only for internal usage within the AWS resources or services, these are very similar to a user, roles are given to machines and the user is going to be a physical person.
IAM Policies are written in JSON documents, which defines what each of the above can and cannot do.
Create an IAM user
Step 1
Login to AWS management console with root user credentials.
Step 2
Search IAM on find services search bar on the management console dashboard.
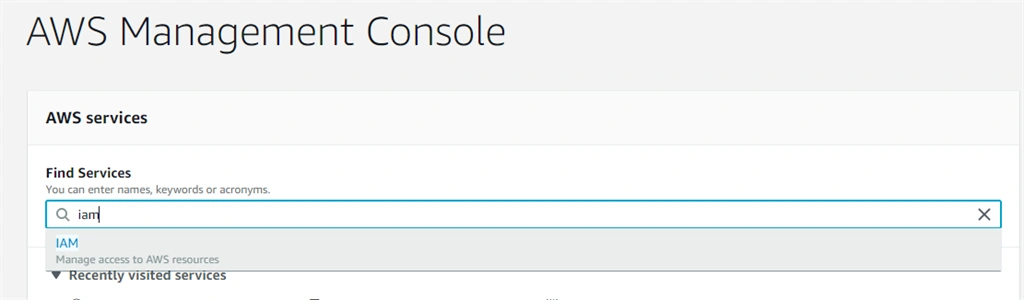
IAM is a global service, IAM users not specific to availability zone its AWS global
Step 3
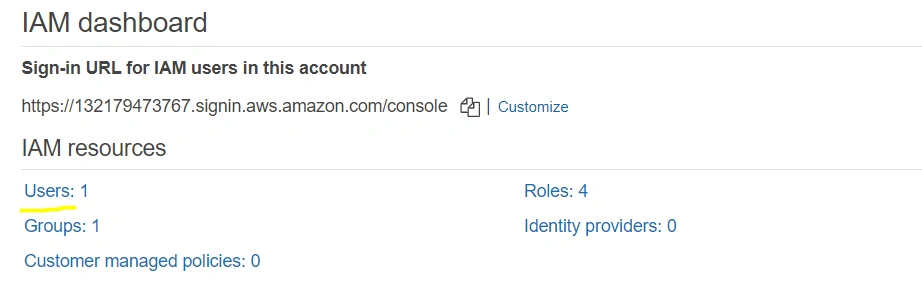
Now we have an IAM dashboard where we need to click on users.
Step 4
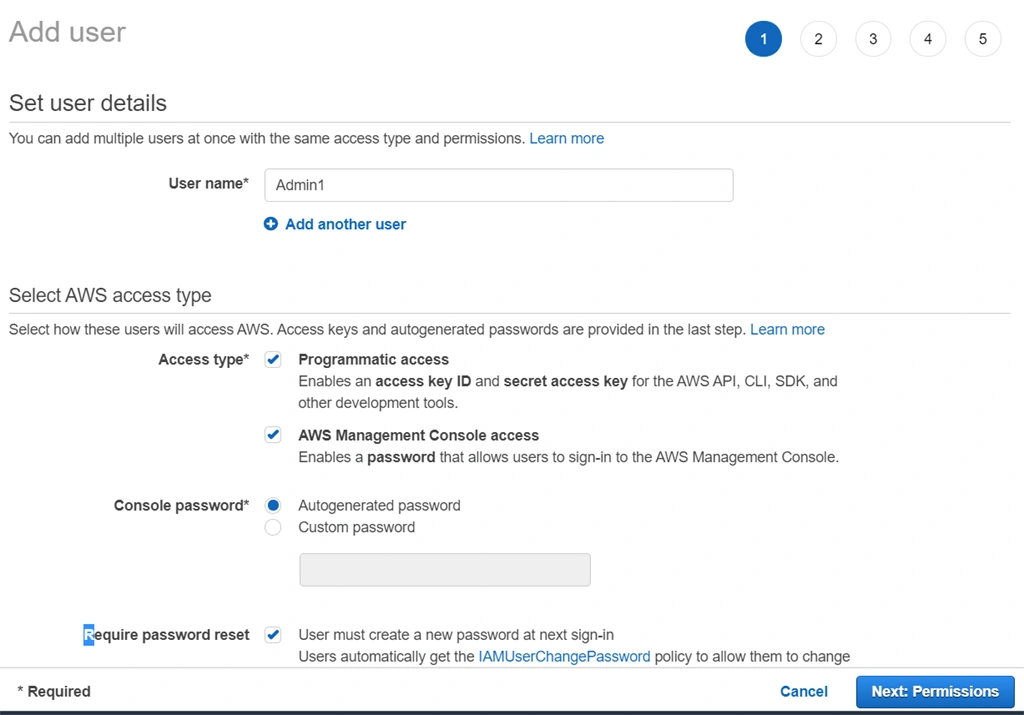
Then click on add user and a screen is open to add a new user and fill the respective details like below where we give both programmatic access and AWS management console access with an autogenerate password and then click on Next: permissions
Step 5
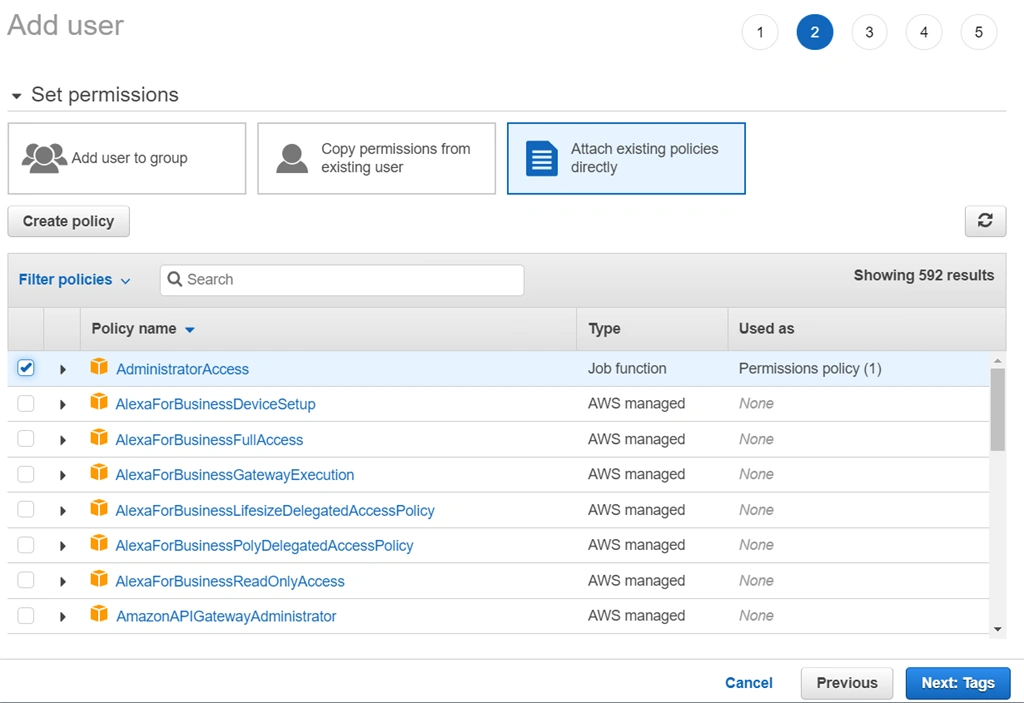
Now we can set permissions in three ways:
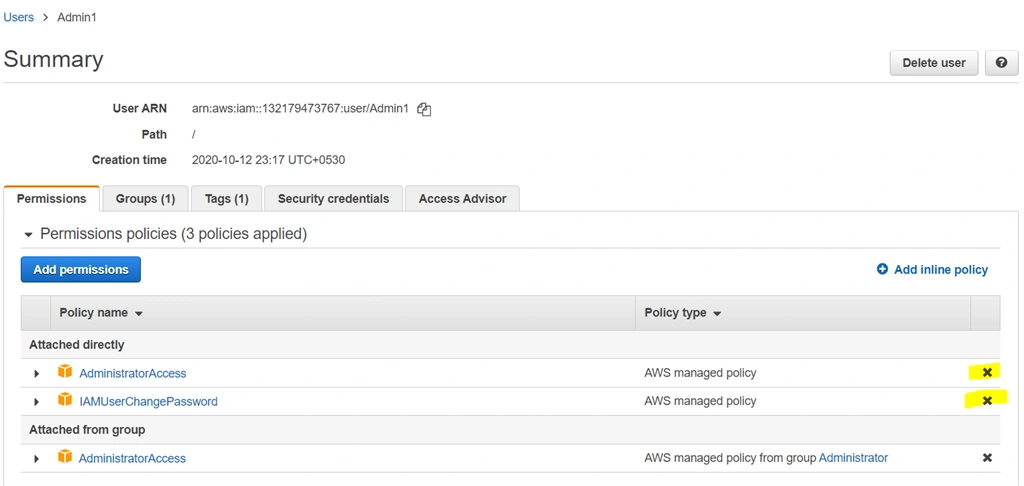
- Add user to the group - Add user to an existing group where the new user will get the same permissions to define in the new group
- Copy permissions from existing users - as the name suggests you will get the same permissions from the copy user.
- Attach existing policies directly - you can define the policies directly from here
Join the conversation! Your thoughts help the community grow.