
Unifying Access: AWS SSO Federation with Okta
As businesses increasingly adopt cloud services, the need for efficient and secure identity and access management becomes paramount. Amazon Web Services (AWS) offers a robust solution in the form of AWS IAM Identity Center formerly known as AWS Single Sign-On (SSO), simplifying access across multiple AWS accounts in AWS Organization and applications. Integrating AWS SSO with Okta, a leading identity management platform, can further enhance user experience and security. In this blog, I’ll talk about concept of AWS SSO Federation with Okta and delve into the architecture that drives this seamless identity management.
The Power of AWS SSO Federation
AWS SSO is designed to streamline access management for multiple AWS accounts and applications. It enables users to sign in once using their existing corporate enterprise credentials and access all their assigned AWS accounts and applications without the need for multiple logins. This not only simplifies the user experience but also reduces administrative overhead and enhances security by enforcing multi-factor authentication (MFA) policies.
AWS IAM Identity Center allows you to
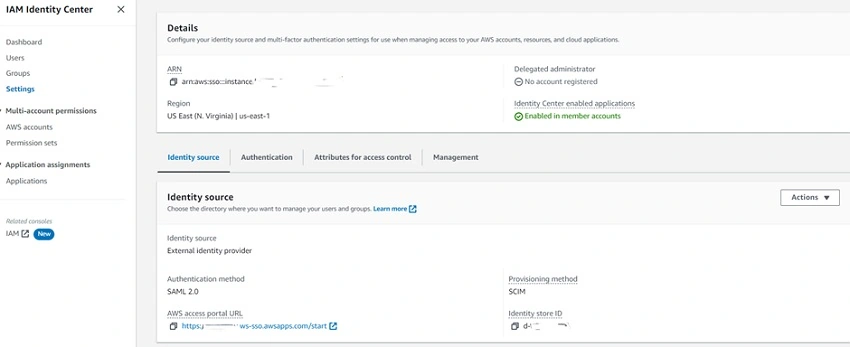
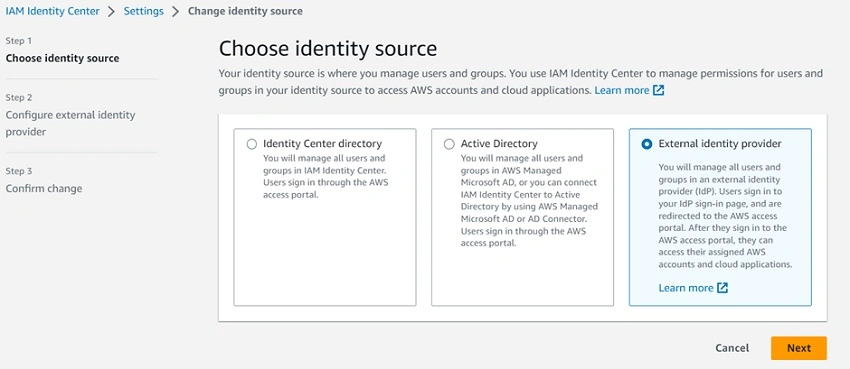
Choose your preferred identity source (Okta One ID) for use across AWS Organization.
- Use multi-account permissions to give workforce users access to multiple AWS accounts or Applications.
- Use the power of application assignments to give your workforce users single sign-on access to AWS and cloud applications.
In the below diagram, we can have multiple identity source options. In this blog, we will talk about OKTA.
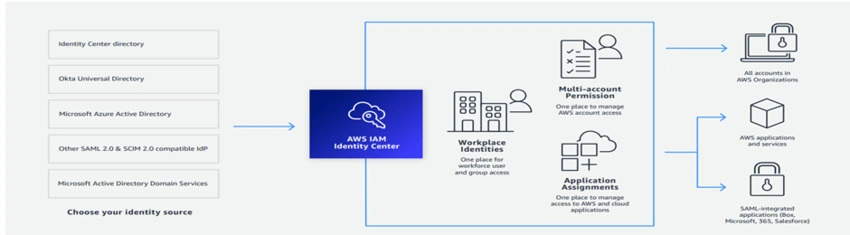
Figure 1.Multiple Identity Providers with AWS IAM Identity Center
Introducing Okta as an Identity Provider
Okta is a modern identity management platform that offers Single Sign-On (SSO), Multi-Factor Authentication (MFA), and centralized user management capabilities. By integrating Okta with AWS SSO, organizations can leverage their existing user identities to seamlessly access AWS resources.
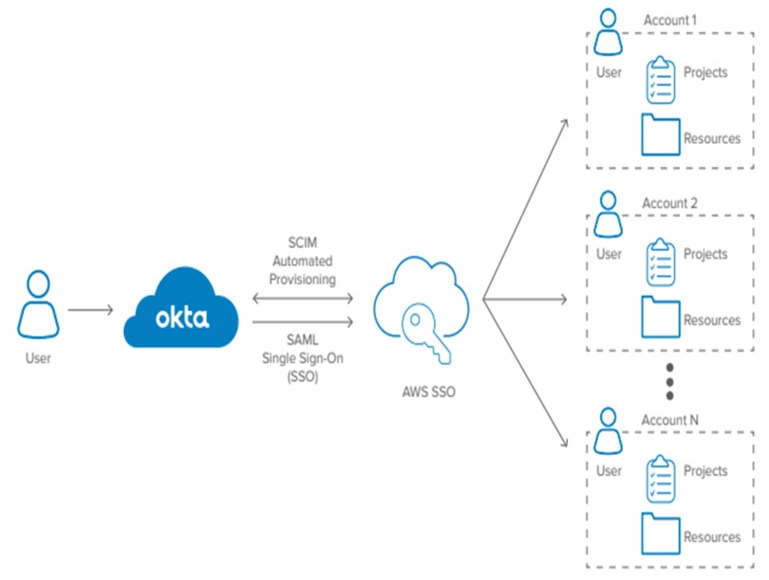
Figure 2. Multi-account integration representation with Okta
AWS IAM Identity Center with Okta -Workflow
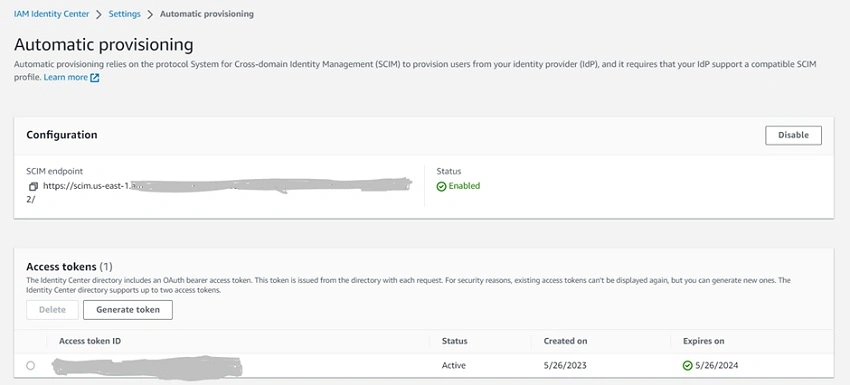
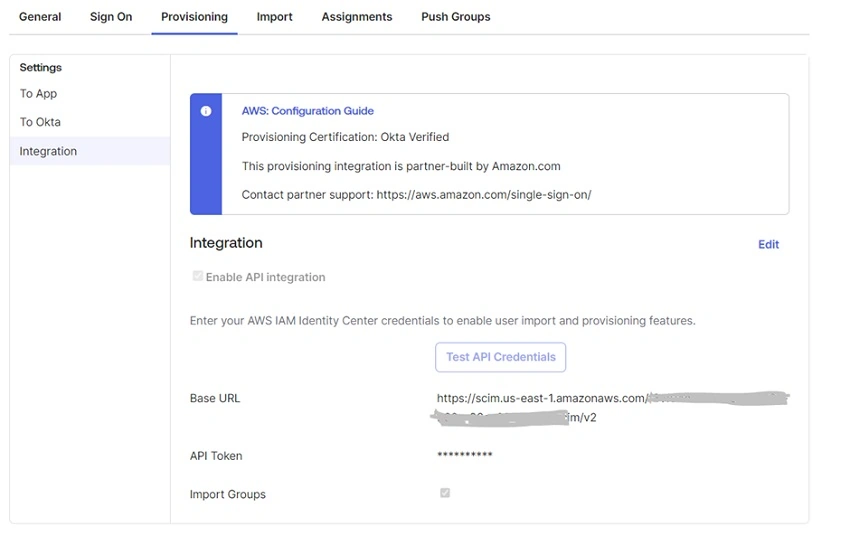
- With Okta One ID Federation, we can automatically provision users and groups into AWS IAM Identity Center using SCIM automated Provisioning.
- AWS SSO centralizes the administration of users and permission sets across all AWS accounts, so admins can more easily manage who gets access to what in AWS.
- Using Okta Lifecycle Management, users and groups defined in Okta are automatically synchronized with AWS SSO. With Okta SSO integration, Project-specific Group management would be performed in Okta IdP.
- AWS SSO admins can then assign permissions sets for those users and groups to authorize access for AWS services (e.g., Amazon EC2, Amazon S3) for specific AWS accounts.
- Changes made in Okta (for example, when someone leaves the org or changes roles) are automatically reflected downstream, through AWS SSO, to change access permissions instantly.
- •Using the Group Push feature, existing Okta groups and their memberships can be pushed to AWS SSO. Then, in AWS SSO, you can create role-oriented permission sets per account, which determines a user’s permissions to access a particular AWS account.
- .The final step is to assign users to AWS accounts and permissions sets. Now when a user signs into the AWS SSO user portal from Okta, they will only gain access (through the AWS management console) to the specific AWS accounts and resources that they are authorized to.
SAML Federation Architecture
The architecture diagram illustrates the AWS SSO Federation with any Identity provider( here it is Okta) flow.
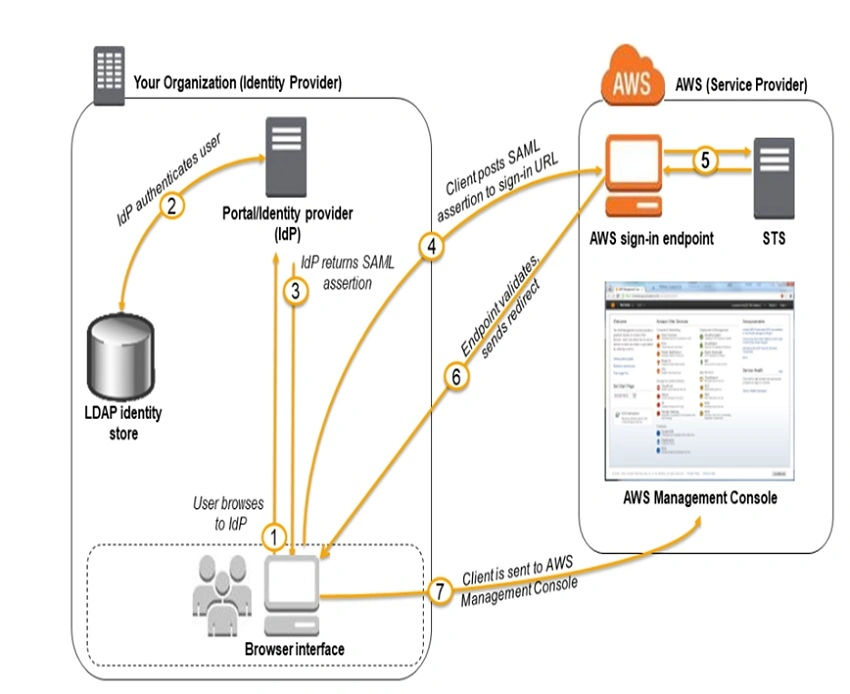
Figure 3
SAML federation workflow with AWS SSO
- User Access Request: The user browses to your organization’s portal and selects the option to go to the AWS Management Console. In your organization, the portal is typically a function of your IdP that handles the exchange of trust between your organization and AWS.
- Okta Authentication: The portal verifies the user’s identity in your organization.
- SAML Assertion Generation: The portal generates a SAML authentication response that includes assertions that identify the user and include attributes about the user. We can also configure your IdP to include a SAML assertion attribute called Session Duration that specifies how long the console session is valid. We can also configure the IdP to pass attributes as session tags. The portal sends this response to the client's browser.
- SAML Assertion Exchange: The client browser is redirected to the AWS single sign-on endpoint and posts the SAML assertion.
- AWS SSO Authentication: The endpoint requests temporary security credentials on behalf of the user and creates a console sign-in URL that uses those credentials.
- Access AWS Resources: The client browser is redirected to the AWS Management Console. If the SAML authentication response includes attributes that map to multiple IAM roles, the user is first prompted to select the role for accessing the console.
Key Advantages of AWS SSO Federation with Okta
- Automatic Provisioning: Automatic provisioning of user and group information from Okta to AWS SSO using the SCIM V2.0 protocol.
- Simplified Access Management: Users can access multiple AWS accounts and applications with a single set of corporate credentials.
- Enhanced Security: Centralized authentication and MFA policies from Okta improve overall security posture.
- Reduced Administrative Overhead: Centralized management of Users/Groups and Permissions from AWS Management account .IT teams spend less time managing user accounts and permissions.
- Auditing and Compliance: Centralized identity management allows for easier tracking and auditing of user access.
- Improved User Experience: Users enjoy a seamless sign-on experience across a diverse range of AWS Accounts and applications.
Join the conversation! Your thoughts help the community grow.